
Oracle certification practice
Free 1Z0-1067-25 Practice Test
10 free 1Z0-1067-25 exam-style questions for Oracle Cloud Infrastructure 2025 Cloud Ops Professional, with answers, explanations and source references.
Full set: 93 questionsSIMULATION Scenario: 3 (Use the OCI CLI to Work with Object Storage from a Compute Instance) Scenario Description: (Hands-On Performance Exam Certification) Your company runs a web application in OCI that generates log files. You want to upload these files to OCI Object Storage to meet data retention requirements. Some files need to be retained indefinitely, whereas others can be deleted after 30 days. Use the OCI CLI to create bucket and upload the log directory and create a lifecycle policy rule to delete temporary files after 30 days. Pre-Configuration: To fulfill this requirement, you are provided with the following: Access to an OCI tenancy, an assigned compartment, and OCI credentials A compute instance with OCI CLI installed and a set of files in ~/dir_to_upload to use Access to the OCI Console Required IAM policies Assumptions: Perform the tasks by using the OCI CLI on the compute instance. Use instance principal authentication for all CLI commands; the instance has been given the policies necessary. Connect to the compute instance using Cloud Shell’s private networking and the provided SSH key. An SSH key pair has been provided to you for the compute instance. Private Key https://objectstorage.us-ashburn1.oraclecloud.com/n/tenancyname/b/PBT_Storage/o/PKey.key Note: Throughout your exam, ensure to use assigned Compartment , User Name and Region. Complete the following tasks in the provisioned OCI environment: Task 1: Create a Bucket in Object Storage Task 2: Upload a Directory’s Contents to Object Storage Task 3: Add a Lifecycle Policy to the Bucket
SIMULATION
Scenario: 1 (Create a reusable VCN Configuration with Terraform)
Scenario Description: (Hands-On Performance Exam Certification)
You’ll launch and destroy a VCN and subnet by creating Terraform automation scripts and issuing
commands in Code Editor. Next, you’ll download those Terraform scripts and create a stack by
uploading them into Oracle Cloud Infrastructure Resource Manager.
You’ll then use that service to launch and destroy the same VCN and subnet.
In this scenario, you will:
a. Create a Terraform folder and file in Code Editor.
b. Create and destroy a VCN using Terraform.
c. Create and destroy a VCN using Resource Manager.
SIMULATION Scenario: 4 (Write Identity and Access Management Policies to Secure a Tenancy) Scenario Description: (Hands-On Performance Exam Certification) Your company has signed up for an OCI tenancy to migrate an e-commerce application, a supply chain management (SCM) system, and a customer relationship management (CRM) system. You have been tasked with setting up the requisite identity and access management (IAM) policies for your team to begin developing on OCI. You start by setting up the following compartment hierarchy: Tenancy (root) Common-Infra Network Security Applications E-Comm SCM CRM You create the following groups: Network-Admins Security-Admins E-Comm-Admins SCM-Admins CRM-Admins Write the IAM policies for the following use cases: Assumptions: Assume that all policies will be attached to the root compartment. Write one policy per given text box. Keep policies as simple as possible by using verbs instead of permissions (for example, “inspect orm-stacks” instead of “ORM_STACK_INSPECT”) and aggregate resource types instead of individual ones (for example, “file-family” instead of “file-systems” and “mount-targets”) Task 1 Write a policy statement to enable Network-Admins to create and destroy network-related resources, such as VCNs, subnets, gateways, and so on in the Network compartment. Task 2 Write policy statements to enable E-Comm-Admins to provision and destroy compute instances in the E-Comm compartment by using networking resources in the Network compartment.[Write one policy per given text box] Task 3 Write a policy statement to enable SCM-Admins to provision, destroy, and back up block volumes in the SCM compartment—but only in Phoenix and London.
Security Testing Policy describes when and how you may conduct certain types of security testing of Oracle Cloud Services, including vulnerability and penetration tests, as well as tests involving data scraping tools. What does Oracle allow as part of this testing? (Choose the best)
You have set an alarm to be generated when the CPU usage of a specified instance is greater than 10%. In the alarm behavior view below you notice that the critical condition happened around 23:30. You were expecting a notification after 1 minute, however, the alarm firing state did not begin until 23:33. 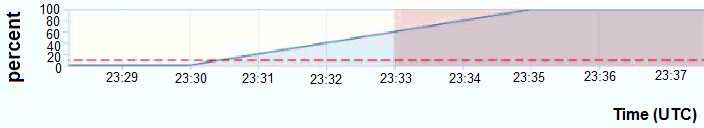 What should you change to fix it? (Choose the best)
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.