CISCO certification preparation

350-201 Practice Questions

Practice exam-style questions, check your answers, and review explanations and source references where they are available.

Exam
350-201
Provider
CISCO
Full set
139 questions
Last Update Check

You need to pass the 350-201 exam to receive your certification. To increase the effectiveness of your study and make you familiar with the actual exam pattern, we have prepared these 350-201 sample questions, complete with answer explanations. Our free 350-201 practice quiz will give you great insight into both the type and difficulty level of the actual questions. However, we strongly recommend practicing with our premium 350-201 exam simulator to achieve the best score. Our premium exam questions are comprehensive, exam-oriented, scenario-based, and an exact match to the real test.

According to GDPR, what should be done with data to ensure its confidentiality, integrity, and availability?
Answer options
A security incident affected an organization’s critical business services, and the customer-side web API became unresponsive and crashed. An investigation revealed a spike of API call requests and a high number of inactive sessions during the incident. Which two recommendations should the engineers make to prevent similar incidents in the future? (Choose two.)
Answer options
An organization had an incident with the network availability during which devices unexpectedly malfunctioned. An engineer is investigating the incident and found that the memory pool buffer usage reached a peak before the malfunction. Which action should the engineer take to prevent this issue from reoccurring?
Answer options
An organization installed a new application server for IP phones. An automated process fetched user credentials from the Active Directory server, and the application will have access to on-premises and cloud services. Which security threat should be mitigated first?
Answer options
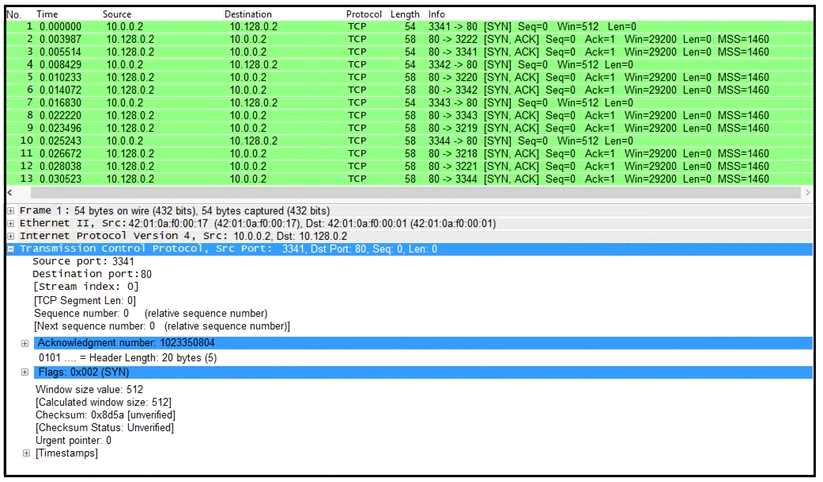
Refer to the exhibit. CISCO 350-201 question What is the threat in this Wireshark traffic capture?
Answer options
What is a limitation of cyber security risk insurance?
Answer options
A SIEM tool fires an alert about a VPN connection attempt from an unusual location. The incident response team validates that an attacker has installed a remote access tool on a user’s laptop while traveling. The attacker has the user’s credentials and is attempting to connect to the network. What is the next step in handling the incident?
Answer options
An audit is assessing a small business that is selling automotive parts and diagnostic services. Due to increased customer demands, the company recently started to accept credit card payments and acquired a POS terminal. Which compliance regulations must the audit apply to the company?
Answer options
What is the difference between process orchestration and automation?
Answer options
An engineer is utilizing interactive behavior analysis to test malware in a sandbox environment to see how the malware performs when it is successfully executed. A location is secured to perform reverse engineering on a piece of malware. What is the next step the engineer should take to analyze this malware?
Answer options
Question 1 of 10

Source context

How this practice set is maintained

Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.

Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.

Scroll to Top