
IBM certification practice
C1000-162 Practice Questions
Try 10 free C1000-162 exam-style questions for IBM Security QRadar SIEM V7.5 Analysis. Check each answer and review the explanation and source references.
- Exam code
- C1000-162
- Provider
- IBM
- Free questions
- 10
- Full set
- 64 questions
- Last update check
Becoming an IBM Security QRadar SIEM V7.5 Analyst is a demanding career milestone that tests your ability to detect, investigate, and analyze complex network threats. Because this cybersecurity exam focuses heavily on real-world threat hunting and rule tuning, relying solely on theoretical reading is rarely enough. That is why utilizing an authentic C1000-162 practice quiz is the smartest strategy to ensure you are fully prepared to handle the intense, scenario-based questions IBM utilizes.
Cert Mage offers an interactive testing platform where you can try free C1000-162 exam questions designed by industry professionals who understand the exact layout of the SIEM assessment. After every session, you can review incredibly detailed answer explanations that dissect the underlying logic of offense analysis and log configuration, helping you learn from every mistake. You are welcome to explore our free IBM PDF questions to establish your baseline, and if you are determined to pass on your first attempt, you can acquire our premium files for unrestricted access to our complete, highly accurate question repository.
DRAG DROP Select all that apply What is the sequence to create and save a new search called "Offense Data" that shows all the CRE events that are associated with offenses? 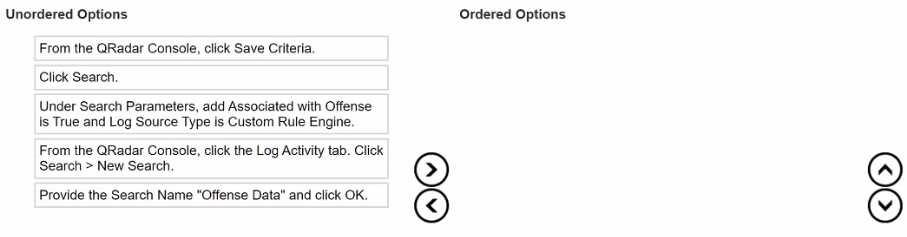
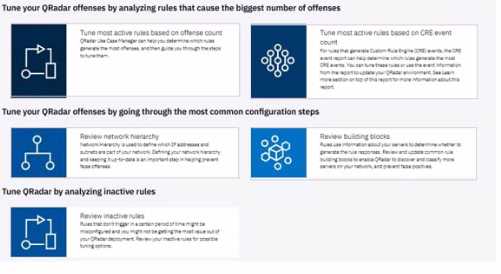
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.