Logical Operations certification practice

CFR-210 Practice Questions

Try 10 free CFR-210 exam-style questions for Certified CyberSec First Responder. Check each answer and review the explanation and source references.

Exam code
CFR-210
Provider
Logical Operations
Free questions
10
Full set
100 questions
Last update check

The CFR-210 exam validates your expertise as a CyberSec First Responder and is a key milestone within the CertNexus credential path. This exam assesses your ability to analyze threats, design secure network architectures, and optimize incident response solutions. Whether you are advancing your career or deepening your technical foundation in cybersecurity, we provide a structured study roadmap and practical resources on this page to help you prepare effectively.
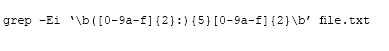
Logical Operations CFR 210 question The above Linux command is used to search for:
Answer options
During a malware outbreak, a security analyst has been asked to capture network traffic in hourly increments for analysis by the incident response team. Which of the following tcpdump commands would generate hourly pcap files?
Answer options
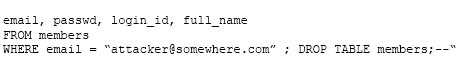
A company website was hacked via the SQL query below: Logical Operations CFR 210 question Which of the following did the hackers perform?
Answer options
A zero-day vulnerability is discovered on a company’s network. The security analyst conducts a log review, schedules an immediate vulnerability scan, and quarantines the infected system, but cannot determine the root cause of the vulnerability. Which of the following is a source of information that can be used to identify the cause of the vulnerability?
Answer options
A network administrator has been asked to configure a new network. It is the company’s policy to segregate network functions using different Virtual LANs (VLANs). On which of the following is this configuration MOST likely to occur?
Answer options
Which of the following describes pivoting?
Answer options
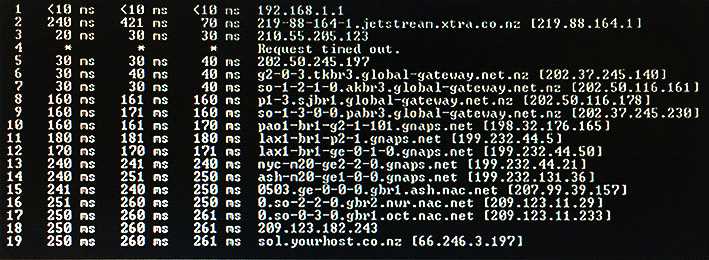
Click the exhibit button. Which of the following Windows tools is executed? Logical Operations CFR 210 question
Answer options
During the identification phase, it is discovered that port 23 is being used maliciously. Which of the following system hardening techniques should be used to remediate the issue?
Answer options
A logfile generated from a Windows server was moved to a Linux system for further analysis. A system administrator is now making edits to the file with vi and notices the file contains numerous instances of Ctrl-M (^M) characters. Which of the following command line tools is the administrator MOST likely to use to remove these characters from the logfile? (Choose two.)
Answer options
An incident responder is asked to work with the IT department to address patch management issues with the company servers. Which of the following is the BEST source for the incident responder to obtain the CVEs for the latest industry-recognized patches?
Answer options
Question 1 of 10

Source context

How this practice set is maintained

Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.

Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.

Scroll to Top