Dell certification practice

D-SF-A-24 Practice Questions

Try 10 free D-SF-A-24 exam-style questions for Dell Security Foundations Achievement. Check each answer and review the explanation and source references.

Exam code
D-SF-A-24
Provider
Dell
Free questions
10
Full set
20 questions
Last update check

This D-SF-A-24 General Practice Test assesses your knowledge in Dell Security Foundations. We cover key concepts such as security framework deployment, access controls, threat mitigation, and data protection processes required to successfully navigate the D-SF-A-24 certification.
A .R.T.I.E. is planning to deploy some of their applications in a public cloud. A major concern is how to share and protect data off premises. Also, how data can be used in decision making without exposing it to anyone who should not have access. Dell Services briefed them about various control mechanisms to secure data in the public cloud. Which control mechanism should be selected in this scenario?
Answer options
Which framework should be recommended to A .R.T.I.E. to enhance the overall security and resilience of their critical infrastructure, and outline methods to reduce their cybersecurity risk?
Answer options
The security team recommends the use of User Entity and Behavior Analytics (UEBA) in order to monitor and detect unusual traffic patterns, unauthorized data access, and malicious activity of A .R.T.I.E. The monitored entities include A .R.T.I.E. processes, applications, and network devices Besides the use of UEBA, the security team suggests a customized and thorough implementation plan for the organization. What are the key attributes that define UEBA?
Answer options
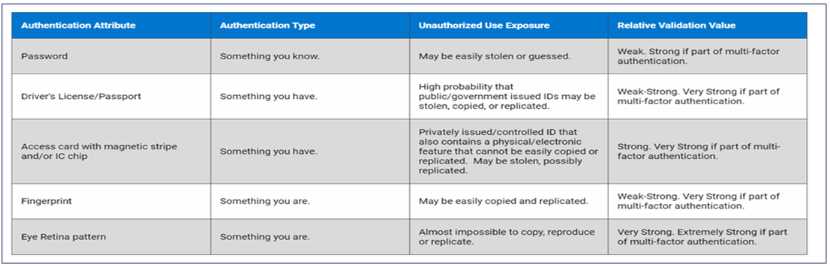
A .R.T.I.E. has an evolving need, which was amplified during the incidents. Their complex and dispersed IT environments have thousands of users, applications, and resources to manage. Dell found that the existing Identity and Access Management was limited in its ability to apply expanding IAM protection to applications beyond the core financial and human resource management application. A .R.T.I.E. also did not have many options for protecting their access especially in the cloud. A .R.T.I.E. were also not comfortable exposing their applications for remote access. Dell recommended adopting robust IAM techniques like mapping out connections between privileged users and admin accounts, and the use multifactor authentication. Dell Security Foundations D SF A 24 question The Dell Services team suggest implementing a system that requires individuals to provide a PIN and biometric information to access their device. Which type of multifactor authentication should be suggested?
Answer options
An A .R.T.I.E. employee received an email with an invoice that looks official for $200 for a one-year subscription. It clearly states: "Please do not reply to this email," but provides a Help and Contact button along with a phone number. What is the type of risk if the employee clicks the Help and Contact button?
Answer options

DRAG DROP Match the security hardening type with the hardening techniques. Dell Security Foundations D SF A 24 question
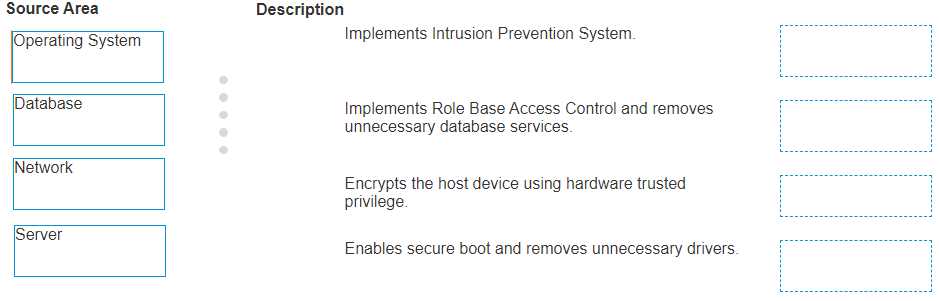
Drag and drop answer

DRAG DROP Dell Services team cannot eliminate all risks, but they can continually evaluate the resilience and preparedness of A .R.T.I.E. by using the National Institute of Standards and Technology Cybersecurity Framework (NIST CSF). Match the core NIST CSF component functions with the description that the Dell Services team would have recommended to A .R.T.I.E. Dell Security Foundations D SF A 24 question
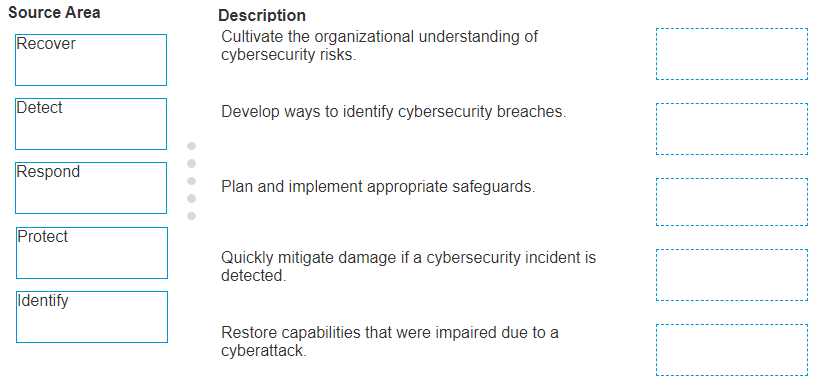
Drag and drop answer

DRAG DROP The cybersecurity team created a detailed security incident management procedures training program to manage any probable incidents at A .R.T.I.E. Arrange the steps in the proper sequence to best manage cybersecurity incidents. Dell Security Foundations D SF A 24 question
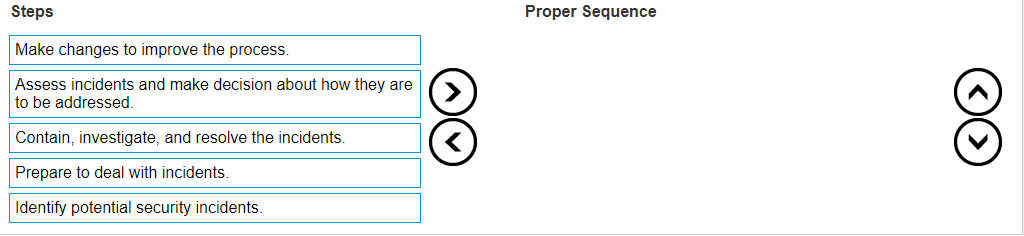
Drag and drop answer
During the analysis, the threat intelligence team disclosed a possible threat which went unnoticed when an A .R.T.I.E. employee sent their friend a slide deck containing the personal information of a colleague. The exposed information included employee first and last names, date of birth and employee ID. What kind of attack occurred?
Answer options
A R.T.I.E.'s business is forecast to grow tremendously in the next year, the organization will not only need to hire new employees but also requires contracting with third-party vendors to continue seamless operations. A .R.T.I.E. uses a VPN to support its employees on the corporate network, but the organization is facing a security challenge in supporting the third-party business vendors. To better meet A .R.T.I.E.'s security needs, the cybersecurity team suggested adopting a Zero Trust architecture (ZTA). The main aim was to move defenses from static, network-based perimeters to focus on users, assets, and resources. Zero Trust continuously ensures that a user is authentic and the request for resources is also valid. ZTA also helps to secure the attack surface while supporting vendor access. What is the main challenge that ZTA addresses?
Answer options
Question 1 of 10

Source context

How this practice set is maintained

Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.

Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.

Scroll to Top