
Fortinet certification practice
FCSS_SOC_AN-7-4 Practice Questions
Try 10 free FCSS_SOC_AN-7-4 exam-style questions for FCSS – Security Operations 7.4 Analyst. Check each answer and review the explanation and source references.
- Exam code
- FCSS_SOC_AN-7-4
- Provider
- Fortinet
- Free questions
- 10
- Full set
- 32 questions
- Last update check
Tackle the specialized security operations topics of the FCSS_SOC_AN-7.4 certification with absolute certainty by utilizing Cert Mage’s premier study materials. Our comprehensive FCSS_SOC_AN-7.4 practice questions are specifically formulated to challenge your understanding of key threat analysis frameworks. Before making any commitments, we encourage you to evaluate your current knowledge base using our free FCSS_SOC_AN-7.4 sample questions. When you are ready to escalate your studies, our intuitive exam simulator and elite FCSS_SOC_AN-7.4 question bank will supply all the authentic exam questions necessary for total mastery of the subject.
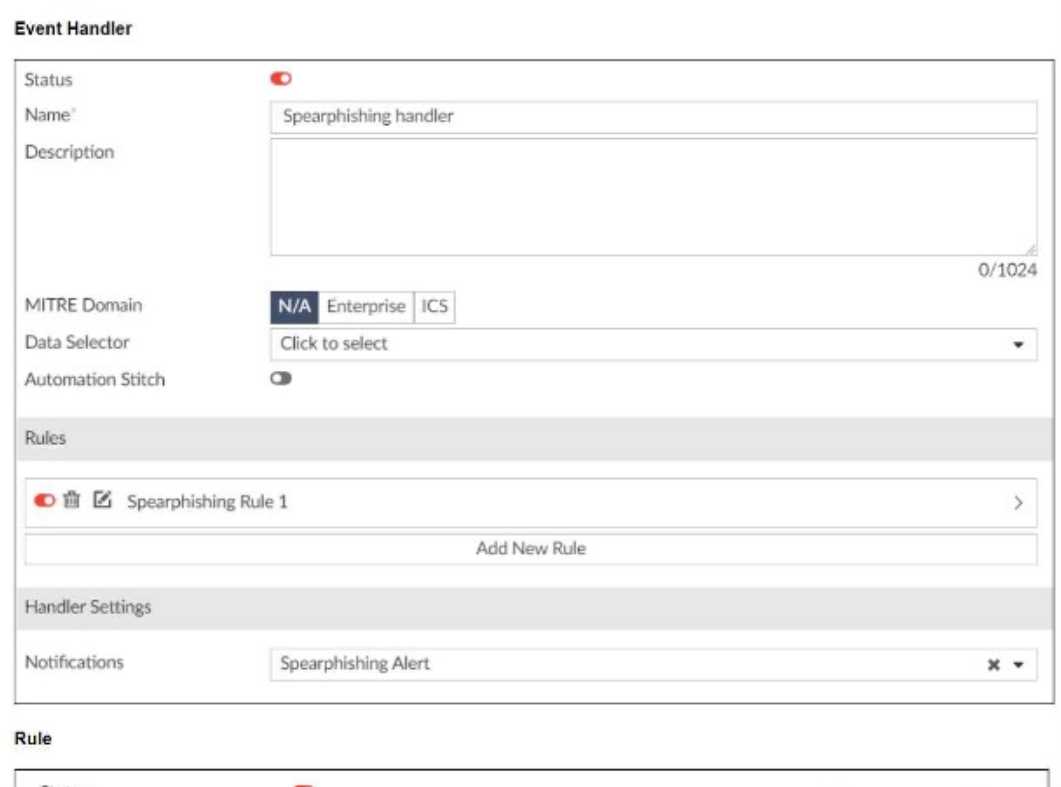 You configured a spearphishing event handler and the associated rule. However. FortiAnalyzer did
not generate an event.
When you check the FortiAnalyzer log viewer, you confirm that FortiSandbox forwarded the
appropriate logs, as shown in the raw log exhibit.
What configuration must you change on FortiAnalyzer in order for FortiAnalyzer to generate an
event?
 A SOC analyst is creating the Malicious File Detected playbook to run when FortiAnalyzer generates a
malicious file event. The playbook must also update the incident with the malicious file event data.
What must the next task in this playbook be?
 You configured a custom event handler and an associated rule to generate events whenever
FortiMail detects spam emails. However, you notice that the event handler is generating events for
both spam emails and clean emails.
Which change must you make in the rule so that it detects only spam emails?
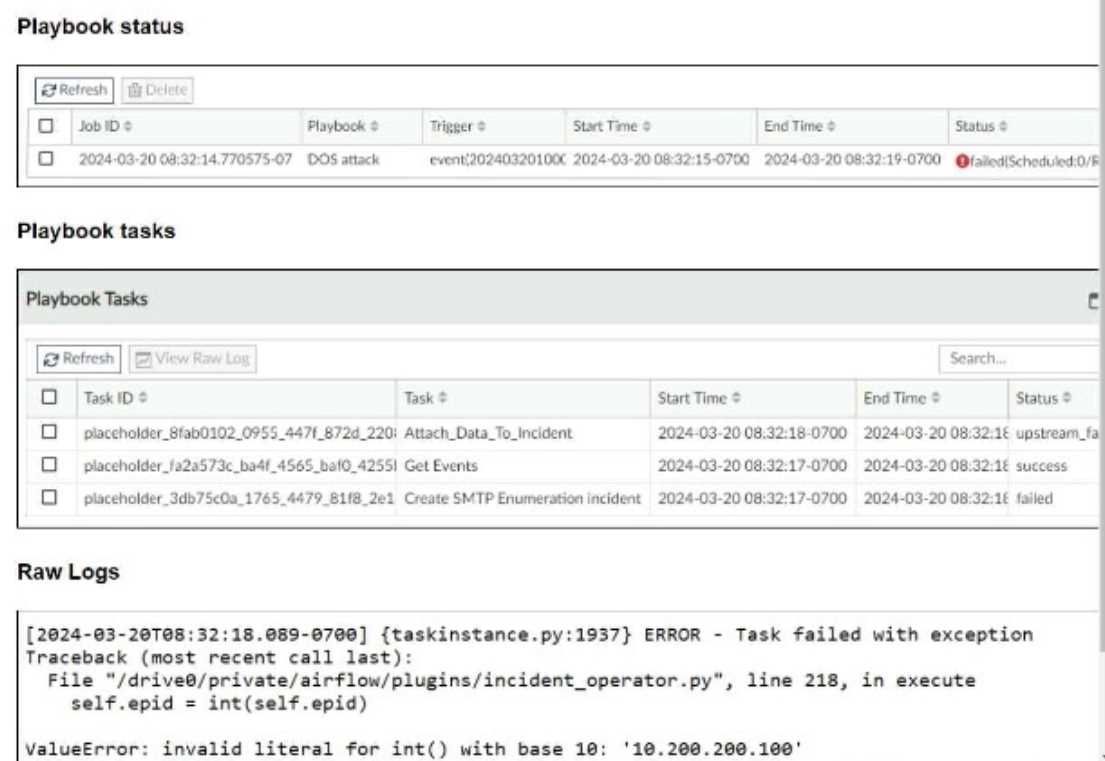 The DOS attack playbook is configured to create an incident when an event handler generates a
denial-of-ser/ice (DoS) attack event.
Why did the DOS attack playbook fail to execute?
 An analyst wants to create an incident and generate a report whenever FortiAnalyzer generates a
malicious attachment event based on FortiSandbox analysis. The endpoint hosts are protected by
FortiClient EMS integrated with FortiSandbox. All devices are logging to FortiAnalyzer.
Which connector must the analyst use in this playbook?
 which shows the partial output of the MITRE ATT&CK Enterprise matrix on FortiAnalyzer.
Which two statements are true? (Choose two.)
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.