
Salesforce certification practice
Free IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT Practice Test
10 free IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam-style questions for Salesforce Certified Platform Identity and Access Management Architect, with answers, explanations and source references.
Full set: 248 questionsThe Salesforce Certified Platform Identity and Access Management Architect exam is for people who design how users sign in and gain access across Salesforce and connected systems. It certifies knowledge of identity management concepts, third-party identity, and the use of Salesforce as an identity provider. The exam has 60 multiple-choice questions, plus up to five unscored questions, with 120 minutes allowed and a passing score of 65%. There are no prerequisites.
Six domains make up the exam. Accepting Third-Party Identity in Salesforce carries the most weight at 21%, followed by Community (Partner and Customer) at 18%. Identity Management Concepts and Salesforce as an Identity Provider each count for 17%, Access Management Best Practices for 15%, and Salesforce Identity for 12%. No single domain dominates, so cover all six, and give extra study time to third-party identity and to partner and customer communities.
Use the free practice questions to test each domain in turn. Check each answer before moving on, and read every explanation, including those for questions you got right. Note whether a missed question involved Salesforce trusting an outside identity provider or acting as one itself, since the exam treats these as separate domains. Then revisit your weak domains and try their questions again.
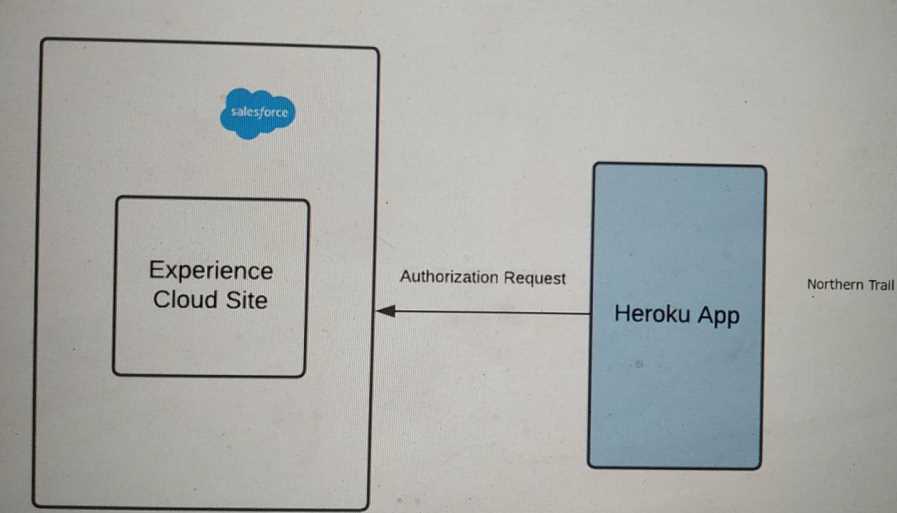 Outfitters (NTO) is using Experience Cloud as an Identity for its application on Heroku. The
application on Heroku should be able to handle two brands, Northern Trail Shoes and Northern Trail
Shirts.
A user should select either of the two brands in Heroku before logging into the community. The app
then performs Authorization using OAuth2.0 with the Salesforce Experience Cloud site.
NTO wants to make sure it renders login page images dynamically based on the user's brand
preference selected in Heroku before Authorization.
what should an identity architect do to fulfill the above requirements?
About the exam
IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam at a glance
Key facts for the Salesforce Certified Platform Identity and Access Management Architect exam, taken from the official exam page.
| Exam code | Summer '23 release alignment |
|---|---|
| Number of questions | 60 |
| Time allowed | 120 minutes |
| Passing score | 65% |
| Question types | Multiple-choice, plus up to five unscored questions |
| Exam price | USD 400 or JPY 60,000 plus applicable taxes; retake USD 200 or JPY 30,000 |
| Delivery | Proctored exam delivered onsite at a testing center or in an online environment |
| Languages | English, Japanese; French and Spanish listed as Coming December 2026 |
| Prerequisites | None |
| Validity and renewal | Annual certification maintenance badge on Trailhead; Architect Maintenance Badge (Winter '26) due December 4, 2026; certification expires if the deadline is missed |
Source: official IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam page. Verified . Prices and policies can change, so confirm with the provider before booking.
Exam objectives
What the IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam covers
The IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam is organized into 6 official domains. Weight shows the share of the exam each domain represents, so spend your study time in proportion.
- Identity Management Concepts 17%
- Accepting Third-Party Identity in Salesforce 21%
- Salesforce as an Identity Provider 17%
- Access Management Best Practices 15%
- Salesforce Identity 12%
- Community (Partner and Customer) 18%
Domains and weights from the official IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam outline.
Quick answers
IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam FAQ
How many questions are on the IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam?
The IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam has 60 questions and gives you 120 minutes to finish. Question types include multiple-choice, plus up to five unscored questions.
What is the passing score for IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT?
You need 65% to pass the Salesforce Certified Platform Identity and Access Management Architect exam.
How much does the IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam cost?
The IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT exam costs USD 400 or JPY 60,000 plus applicable taxes; retake USD 200 or JPY 30,000. Check the official exam page for the price in your country.
How long is the IDENTITY-AND-ACCESS-MANAGEMENT-ARCHITECT certification valid?
Annual certification maintenance badge on Trailhead; Architect Maintenance Badge (Winter '26) due December 4, 2026; certification expires if the deadline is missed.
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.
Reviewed by Alexandra Stone CISSP, CISM, CISA, Security+, CEH