
FORTINET certification preparation
NSE8_812 Practice Questions
Practice exam-style questions, check your answers, and review explanations and source references where they are available.
- Exam
- NSE8_812
- Provider
- FORTINET
- Full set
- 105 questions
- Last Update Check
Prepare for the Fortinet NSE 8 Written Exam NSE8_812 with authentic practice questions and interactive quizzes provided by Cert Mage. Try our free NSE8_812 exam questions today to test your knowledge and see exactly where your skills stand. Once you evaluate the quality of our preparation materials, you can easily upgrade to gain full access to the most updated NSE8_812 questions, alongside detailed answers and comprehensive explanations.
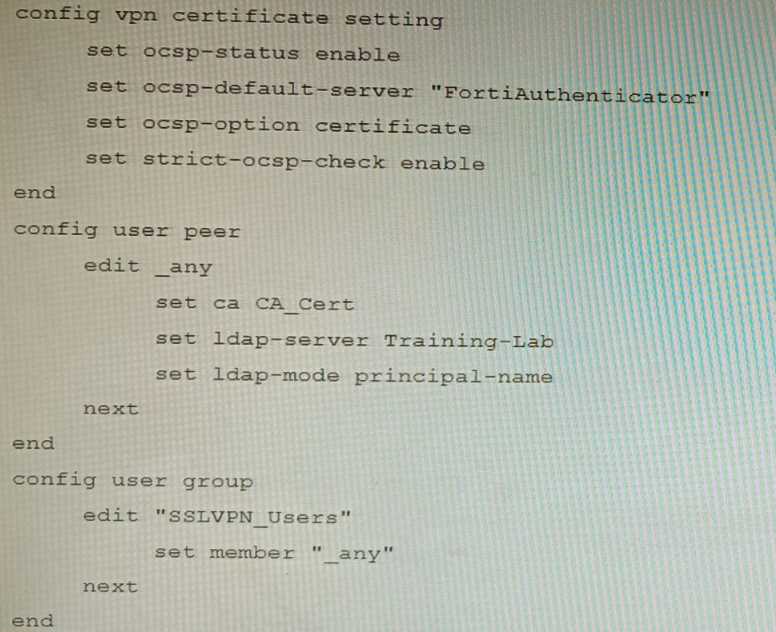 Based on this configuration, which two statements are true? (Choose two.)
Question 1 discussion
 The exhibits show a diagram of a requested topology and the base IPsec configuration.
A customer asks you to configure ADVPN via two internet underlays. The requirement is that you use
one interface with a single IP address on DC FortiGate.
In this scenario, which feature should be implemented to achieve this requirement?
Question 2 discussion
Question 3 discussion
 An administrator has configured a FortiGate and Forti Authenticator for two-factor authentication
with FortiToken push notifications for their SSL VPN login. Upon initial review of the setup, the
administrator has discovered that the customers can manually type in their two-factor code and
authenticate but push notifications do not work
Based on the information given in the exhibits, what must be done to fix this?
Question 4 discussion
 The exhibits show the configuration and debug output from a FortiGate Public SDN Connector.
What is a possible reason for this dynamic address object to be empty?
Question 5 discussion
 Based on this configuration, which authentication scenario will FortiGate deny?
Question 6 discussion
 An HTTPS access proxy is configured to demonstrate its function as a reverse proxy on behalf of the
web server it is protecting. It verifies user identity, device identity, and trust context, before granting
access to the protected source. It is assumed that the FortiGate EMS fabric connector has already
been successfully connected.
You need to ensure that ZTNA access through the FortiGate will redirect users to the
FortiAuthenticator to perform username/password and multifactor authentication to validate access
prior to accessing resources behind the FortiGate.
In this scenario, which two further steps need to be taken on the FortiGate? (Choose two.)
Question 7 discussion
Question 8 discussion
Question 9 discussion
 An administrator has configured an inbound SSL inspection profile on a FortiGate device (FG-1) that is
protecting a data center hosting multiple web pages-Given the scenario shown in the exhibits, which
certificate will FortiGate use to handle requests to xyz.com?
Question 10 discussion
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.