Arcitura certification preparation

S90-20 Practice Questions

Practice exam-style questions, check your answers, and review explanations and source references where they are available.

Exam
S90-20
Provider
Arcitura
Full set
30 questions
Last Update Check

Is it difficult for you to decide whether to purchase Arcitura S90-20 exam questions for your certification prep? Cert Mage provides free online SOA Security Lab S90-20 sample questions right below so you can test your hands-on security skills first before making any decisions. We promise that once you try these queries, you will clearly see the advantages of buying the full premium version to unlock all the advanced testing features.
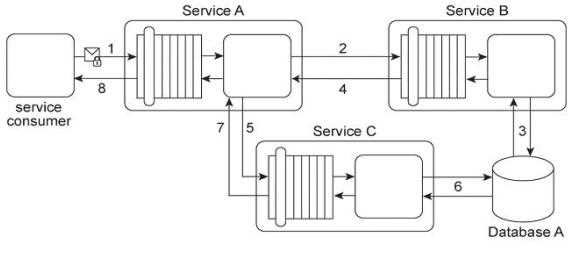
Service A provides a customized report generating capability. Due to infrastructure limitations, the number of service consumers permitted to access Service A concurrently is strictly controlled. Service A validates request messages based on the supplied credentials (1). If the authentication of the request message is successful, Service A sends a message to Service B (2) to retrieve the required data from Database A (3). Service A stores the response from Service B (4) in memory and then issues a request message to Service C (5). Service C retrieves a different set of data from Database A (6) and sends the result back to Service A (7). Service A consolidates the data received from Services B and C and sends the generated report in the response message to its service consumer (8). Arcitura S90 question This service composition was recently shut down after it was discovered that Database A had been successfully attacked twice in a row. The first type of attack consisted of a series of coordinated request messages sent by the same malicious service consumer, with the intention of triggering a range of exception conditions within the database in order to generate various error messages. The second type of attack consisted of a service consumer sending request messages with malicious input with the intention of gaining control over the database server. This attack resulted in the deletion of database records and tables. An investigation revealed that both attacks were carried out by malicious service consumers that were authorized. How can the service composition security architecture be improved to prevent these types of attacks?
Answer options
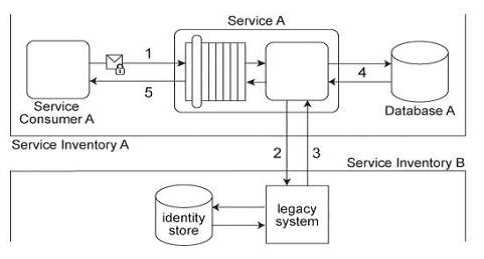
Service Consumer A submits a request message with security credentials to Service A (1). The identity store that Service A needs to use in order to authenticate the security credentials can only be accessed via a legacy system that resides in a different service inventory. Therefore, to authenticate Service Consumer A, Service A must first forward the security credentials to the legacy system (2). The legacy system then returns the requested identity to Service A (3). Service A authenticates Service Consumer A against the identity received from the legacy system. If the authentication is successful, Service A retrieves the requested data from Database A (4), and returns the data in a response message sent back to Service Consumer A (5). Service A belongs to Service Inventory A which further belongs to Security Domain A and the legacy system belongs to Service Inventory B which further belongs to Security Domain B .(The legacy system is encapsulated by other services within Service Inventory B, which are not shown in the diagram.) These two security domains trust each other. Communication between Service A and the legacy system is kept confidential using transport-layer security. It was recently discovered that a malicious attacker, posing as Service Consumer A, has been accessing Service A .An investigation revealed that these attacks occurred because security credentials supplied by Service Consumer A were transmitted in plaintext. Furthermore, vulnerabilities to replay attacks and malicious intermediaries have been detected. Which of the following statements describes a solution that can counter these types of attacks? Also, list the industry standards required by the proposed solution. Arcitura S90 question
Answer options
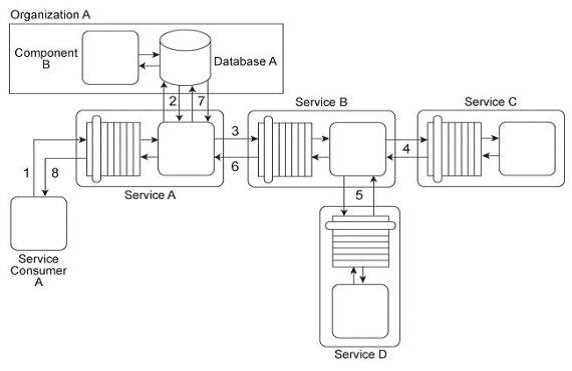
Service Consumer A sends a request message to Service A (1) after which Service A retrieves financial data from Database A (2). Service A then sends a request message with the retrieved data to Service B (3). Service B exchanges messages with Service C (4) and Service D (5), which perform a series of calculations on the data and return the results to Service A .Service A uses these results to update Database A (7) and finally sends a response message to Service Consumer A (8). Component B has direct, independent access to Database A and is fully trusted by Database A .Both Component B and Database A reside within Organization A .Service Consumer A and Services A, B, C, and D are external to the organizational boundary of Organization A . Arcitura S90 question Component B is considered a mission critical program that requires guaranteed access to and fast response from Database A .Service A was recently the victim of a denial of service attack, which resulted in Database A becoming unavailable for extended periods of time (which further compromised Component B). Additionally, Services B, C, and D have repeatedly been victims of malicious intermediary attacks, which have further destabilized the performance of Service A .How can this architecture be improved to prevent these attacks?
Answer options
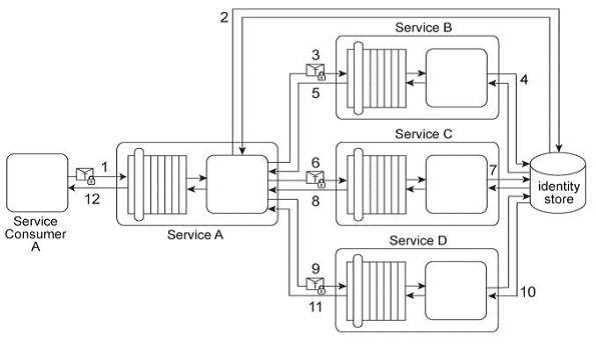
Service Consumer A sends a request message with a Username token to Service A (1). Service B authenticates the request by verifying the security credentials from the Username token with a shared identity store (2), To process Service Consumer A's request message. Service A must use Services B, C, and D .Each of these three services also requires the Username token (3. 6, 9) in order to authenticate Service Consumer A by using the same shared identity store (4, 7, 10). Upon each successful authentication, each of the three services (B, C, and D) issues a response message back to Service A (5, 8, 11). Upon receiving and processing the data in all three response messages, Service A sends its own response message to Service Consumer A (12). There are plans implement a single sign-on security mechanism in this service composition architecture. The service contracts for Services A, C, and D can be modified with minimal impact in order to provide support for the additional messaging requirements of the single sign-on mechanism. However, Service B's service contract is tightly coupled to its implementation and, as a result, this type of change to its service contract is not possible as it would require too many modifications to the underlying service implementation. Given the fact that Service B's service contract cannot be changed to support single sign-on, how can a single sign-on mechanism still be implemented across all services? Arcitura S90 question
Answer options
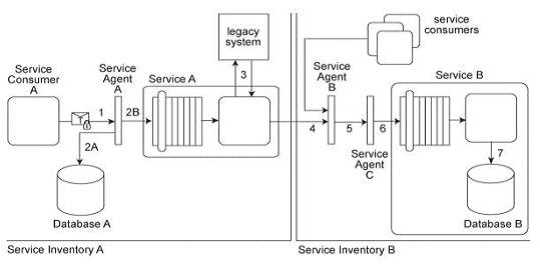
Service Consumer A sends a request message with an authentication token to Service A, but before the message reaches Service A, it is intercepted by Service Agent A (1). Service Agent A validates the security credentials and also validates whether the message is compliant with Security Policy A .If either validation fails, Service Agent A rejects the request message and writes an error log to Database A (2A). If both validations succeed, the request message is sent to Service A (2B). Service A retrieves additional data from a legacy system (3) and then submits a request message to Service B Before arriving at Service B, the request message is intercepted by Service Agent B (4) which validates its compliance with Security Policy SIB then Service Agent C (5) which validates its compliance with Security Policy B .If either of these validations fails, an error message is sent back to Service A .that then forwards it to Service Agent A so that it the error can be logged in Database A (2A). If both validations succeed, the request message is sent to Service B (6). Service B subsequently stores the data from the message in Database B (7). Service A and Service Agent A reside in Service Inventory A .Service B and Service Agents B and C reside in Service Inventory B .Security Policy SIB is used by all services that reside in Service Inventory B .Service B can also be invoked by other service consumers from Service Inventory B .Request messages sent by these service consumers must also be compliant with Security Policies SIB and B .Access to the legacy system in Service Inventory A is currently only possible via Service A, which means messages must be validated for compliance with Security Policy A .A new requirement has emerged to allow services from Service Inventory B to access the legacy system via a new perimeter service that will be dedicated to processing request messages from services residing in Service Inventory B .Because the legacy system has no security features, all security processing will need to be carried out by the perimeter service. However, there are parts of Security Policy A that are specific to Service A and do not apply to the legacy system or the perimeter service. Furthermore, response messages sent by the perimeter service to services from Service Inventory B will still need to be validated for compliance to Security Policy B and Security Policy SIB .How can the Policy Centralization pattern be correctly applied without compromising the policy compliance requirements of services in both service inventories? Arcitura S90 question
Answer options
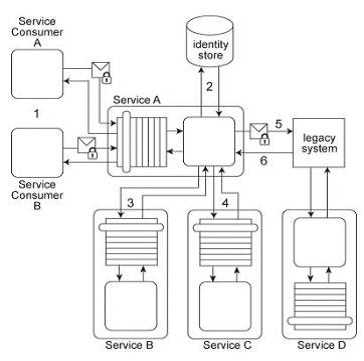
Service A has two specific service consumers, Service Consumer A and Service Consumer B (1). Both service consumers are required to provide security credentials in order for Service A to perform authentication using an identity store (2). If a service consumer's request message is successfully authenticated, Service A processes the request by exchanging messages with Service B (3) and then Service C (4). With each of these message exchanges, Service A collects data necessary to perform a query against historical data stored in a proprietary legacy system. Service A's request to the legacy system must be authenticated (5). The legacy system only provides access control using a single account. If the request from Service A is permitted, it will be able to access all of the data stored in the legacy system. If the request is not permitted, none of the data stored in the legacy system can be accessed. Upon successfully retrieving the requested data (6), Service A generates a response message that is sent back to either Service Consumer A or B .The legacy system is also used independently by Service D without requiring any authentication. Furthermore, the legacy system has no auditing feature and therefore cannot record when data access from Service A or Service D occurs. If the legacy system encounters an error when processing a request, it generates descriptive error codes. This service composition architecture needs to be upgraded in order to fulfill the following new security requirements: 1. Service Consumers A and B have different access permissions and therefore, data received from the legacy system must be filtered prior to issuing a response message to one of these two service consumers. 2. Service Consumer A's request messages must be digitally signed, whereas request messages from Service Consumer B do not need to be digitally signed. Which of the following statements describes a solution that fulfills these requirements? Arcitura S90 question
Answer options
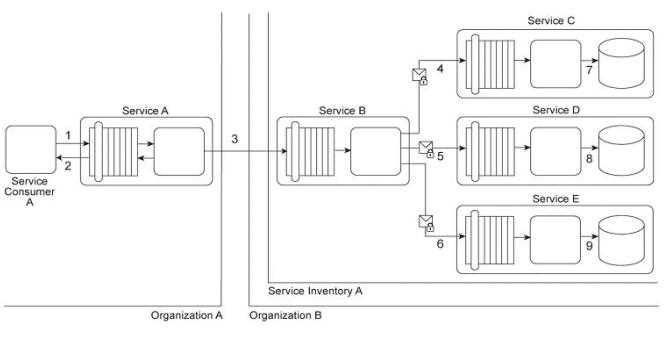
Service Consumer A sends a request to Service A (1). Service A replies with an acknowledgement message (2) and then processes the request and sends a request message to Service B (3). This message contains confidential financial data. Service B sends three different request messages together with its security credentials to Services C .D .and E (4, 5, 6). Upon successful authentication, Services C .D .and E store the data from the message in separate databases (7.8, 9). Services B .C .D, and E belong to Service Inventory A, which further belongs to Organization B .Service Consumer A and Service A belong to Organization A .Organization B decides to create a new service inventory (Service Inventory B) for services that handle confidential data. Access to these services is restricted by allocating Service Inventory B its own private network. Access to this private network is further restricted by a dedicated firewall. Services C, D and E are moved into Service Inventory B, and as a result. Service B can no longer directly access these services. How can this architecture be changed to allow Service B to access Services C, D and E in a manner that does not jeopardize the security of Service Inventory B while also having a minimal impact on the service composition's performance? Arcitura S90 question
Answer options
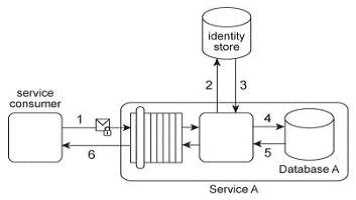
Service A provides a data access capability that can be used by a variety of service consumers. The database records accessed by Service A are classified as either private or public. There are two types of service consumers that use Service A: Service consumers with public access permissions (allowed to access only public data records) and service consumers with private access permissions (allowed to access all data records). For performance reasons the Service A architecture uses a single database, named Database A .Each record in Database A is classified as either private or public. After Service A is invoked by a service consumer (1), it authenticates the request message using an identity store and retrieves the corresponding authorization (2, 3). Once authorized, the service consumer's request is submitted to Database A (4), which then returns the requested data (5) If the service consumer has private access permissions, all of the returned data is included in Service A's response message (6). If the service consumer has public access permissions, then Service A first filters the data in order to remove all unauthorized private data records, before sending to the response message to the service consumer (6). An investigation recently detected that private data has been leaked to unauthorized service consumers. An audit of the Service A architecture revealed that Service A's filtering logic is flawed, resulting in situations where private data was accidentally shared with service consumers that only have public access permissions. Further, it was discovered that attackers have been monitoring response messages sent by Service A in order to capture private data. It is subsequently decided to split Database A into two databases: one containing only private data (the Private Database) and the other containing only public data (the Public Database). What additional changes are necessary to address these security problems? Arcitura S90 question
Answer options
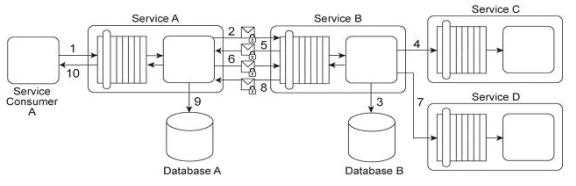
Service Consumer A sends a request message to Service A (1), after which Service A sends a request message with security credentials to Service B (2). Service B authenticates the request and, if the authentication is successful, writes data from the request message into Database B (3). Service B then sends a request message to Service C (4), which is not required to issue a response message. Service B then sends a response message back to Service A (5). After processing Service B's response, Service A sends another request message with security credentials to Service B (6). After successfully authenticating this second request message from Service A, Service B sends a request message to Service D (7). Service D is also not required to issue a response message. Finally, Service B sends a response message to Service A (8), after which Service A records the response message contents in Database A (9) before sending its own response message to Service Consumer A (10). To use Service A, Service Consumer A is charged a per usage fee. The owner of Service Consumer A has filed a complaint with the owner of Service A, stating that the bills that have been issued are for more usage of Service A than Service Consumer A actually used. Additionally, it has been discovered that malicious intermediaries are intercepting and modifying messages being sent from Service B to Services C and D .Because Services C and D do not issue response messages, the resulting errors and problems were not reported back to Service B .Which of the following statements describes a solution that correctly addresses these problems? Arcitura S90 question
Answer options
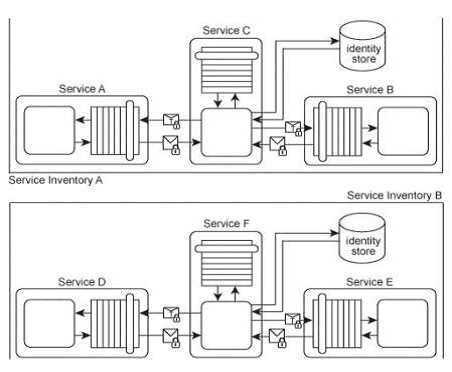
Services A, B and C belong to Service Inventory A .Services D, E and F belong to Service Inventory B .Service C acts as an authentication broker for Service Inventory A .Service F acts as an authentication broker for Service Inventory B .Both of the authentication brokers use Kerberos-based authentication technologies. Upon receiving a request message from a service consumer, Services C and F authenticate the request using a local identity store and then use a separate Ticket Granting Service (not shown) to issue the Kerberos ticket to the service consumer. Currently, tickets issued in one service inventory are not valid in the other. For example, if Service A wants to communicate with Services D or E, it must request a ticket from the Service Inventory B authentication broker (Service F). Because Service Inventory A and B trust each other, the current cross-inventory authentication is considered unnecessarily redundant. How can these service inventory architectures be improved to avoid redundant authentication? Arcitura S90 question
Answer options
Question 1 of 10

Source context

How this practice set is maintained

Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.

Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.

Scroll to Top