
Microsoft certification practice
SC-200 Practice Questions
Try 10 free SC-200 exam-style questions for Microsoft Security Operations Analyst. Check each answer and review the explanation and source references.
- Exam code
- SC-200
- Provider
- Microsoft
- Free questions
- 10
- Full set
- 370 questions
- Last update check
The SC-200 certification is designed for professionals who need to master the core concepts of this field. This exam validates your ability to successfully deploy and manage related technologies. Whether you are advancing your career or building deeper technical expertise, we provide a clear roadmap for focused, effective preparation on this page. Try our free SC-200 practice questions with answer explanations below to test your skills, and use our premium SC-200 question bank to prepare with complete confidence.
Domain Mitigate threats using Microsoft Defender XDR
DRAG DROP You are informed of a new common vulnerabilities and exposures (CVE) vulnerability that affects your environment. You need to use the Microsoft Defender portal to request remediation from the team responsible for the affected systems if there is a documented active exploit available. Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. 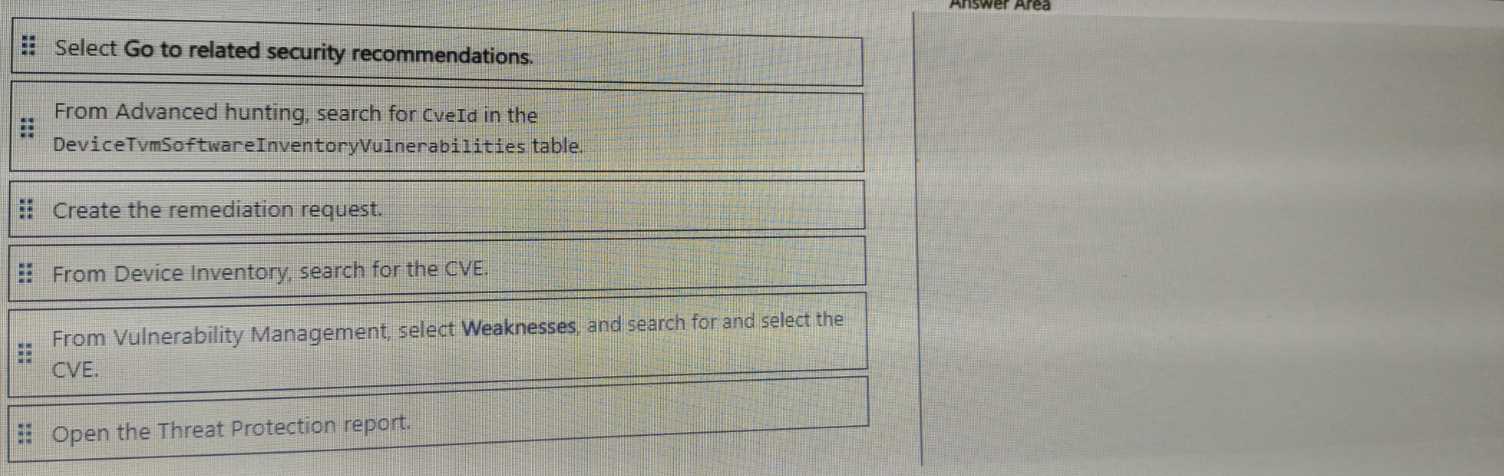
Domain Mitigate threats using Microsoft Defender XDR
Domain Mitigate threats using Microsoft Sentinel
HOTSPOT You need to implement the ASIM query for DNS requests. The solution must meet the Microsoft Sentinel requirements. How should you configure the query? To answer, select the appropriate options in the answer are a. 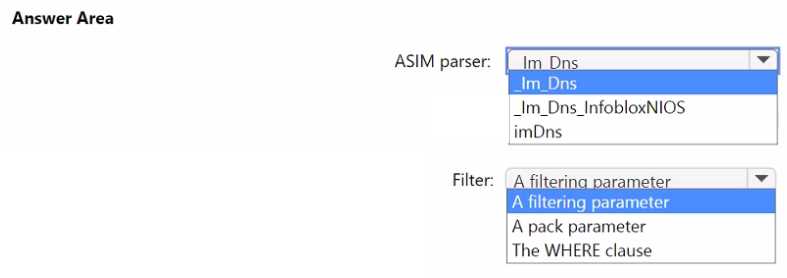
Domain Mitigate threats using Microsoft Sentinel
DRAG DROP Your network contains an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure AD tenant. You have a Microsoft Sentinel workspace named Sentinel1. You need to enable User and Entity Behavior Analytics (UEBA) for Sentinel1 and collect security events from the AD DS domain. Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. 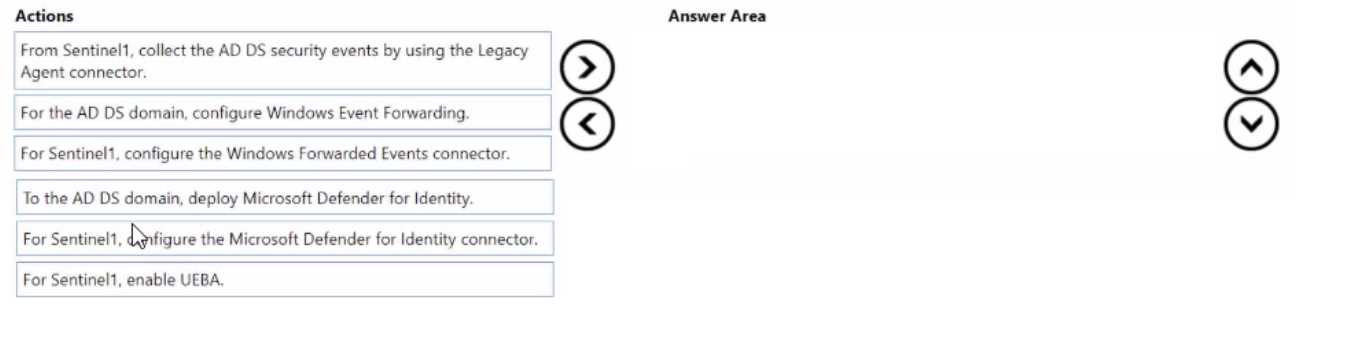
Domain Mitigate threats using Microsoft Defender XDR
DRAG DROP You are informed of a new common vulnerabilities and exposures (CVE) vulnerability that affects your environment. You need to use Microsoft Defender Security Center to request remediation from the team responsible for the affected systems if there is a documented active exploit available. Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order. 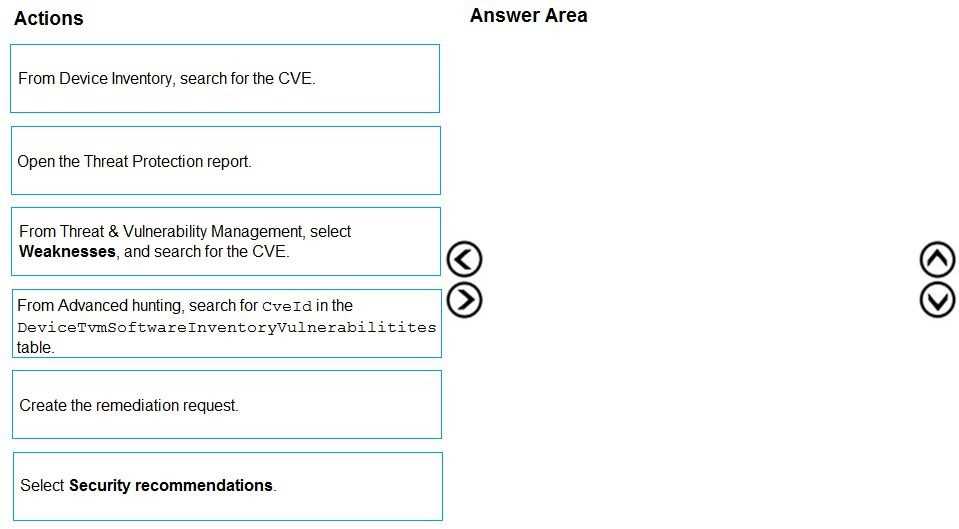
Domain Mitigate threats using Microsoft Sentinel
HOTSPOT You have a Microsoft Sentinel workspace You develop a custom Advanced Security information Model (ASIM) parser named Parser1 that produces a schema named Schema1. You need to validate Schema1. How should you complete the command? To answer, select the appropriate options in the answer area.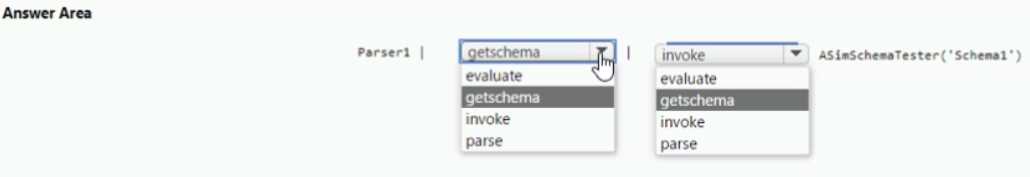
Domain Mitigate threats using Microsoft Defender XDR
DRAG DROP You are investigating an incident by using Microsoft 365 Defender. You need to create an advanced hunting query to detect failed sign-in authentications on three devices named CFOLaptop, CEOLaptop, and COOLaptop. How should you complete the query? To answer, select the appropriate options in the answer area. 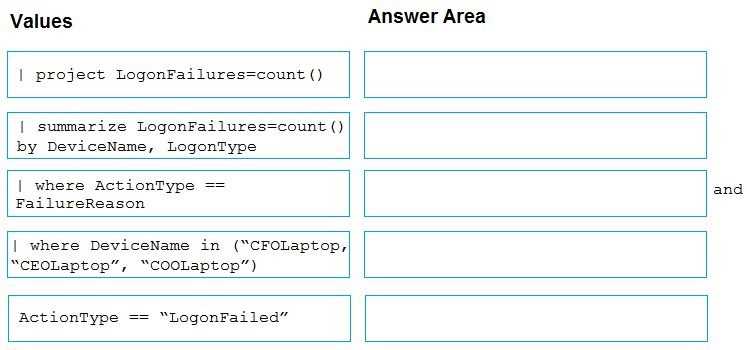
Domain Mitigate threats using Microsoft Sentinel
Domain Mitigate threats using Microsoft Defender for Cloud
DRAG DROP You create a new Azure subscription and start collecting logs for Azure Monitor. You need to validate that Microsoft Defender for Cloud will trigger an alert when a malicious file is present on an Azure virtual machine running Windows Server. Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order. NOTE: More than one order of answer choices is correct. You will receive credit for any of the correct orders you select. 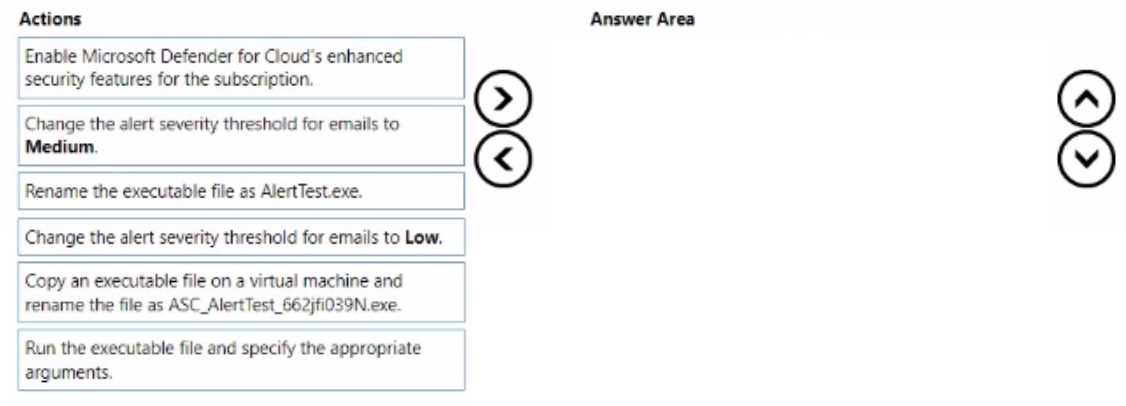
Domain Mitigate threats using Microsoft Defender XDR
Exam domains
What the SC-200 practice set covers
Every question in this set is mapped to one of 3 exam domains. Check the official exam outline for the current domain weights.
Mitigate threats using Microsoft Defender XDR
5 of the 10 free questions
Mitigate threats using Microsoft Defender for Cloud
1 of the 10 free questions
Mitigate threats using Microsoft Sentinel
4 of the 10 free questions
Study resources
SC-200 study guides and comparisons
Go deeper than the practice questions: certification comparisons, study plans, and career context for SC-200.
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.