
Linux Foundation certification practice
Free CKS Practice Test
10 free CKS exam-style questions for Linux Foundation CKS certification exam, with answers, explanations and source references.
Full set: 48 questions Context
A CIS Benchmark tool was run against the kubeadm-created cluster and found multiple issues that
must be addressed immediately.
Task
Fix all issues via configuration and restart the affected components to ensure the new settings take
effect.
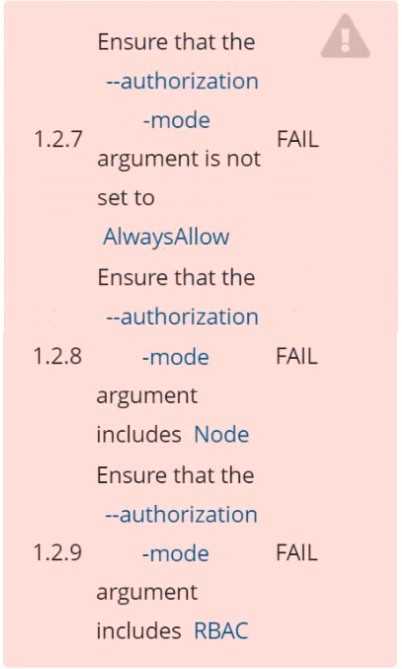
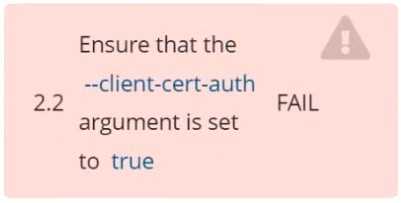
Fix all of the following violations that were found against the API server:
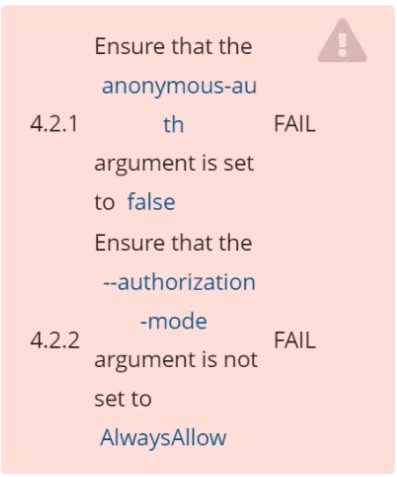
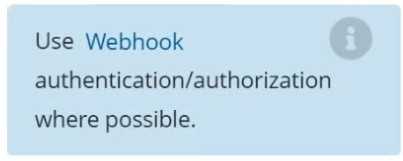
 Fix all of the following violations that were found against the Kubelet:
 Fix all of the following violations that were found against etcd:
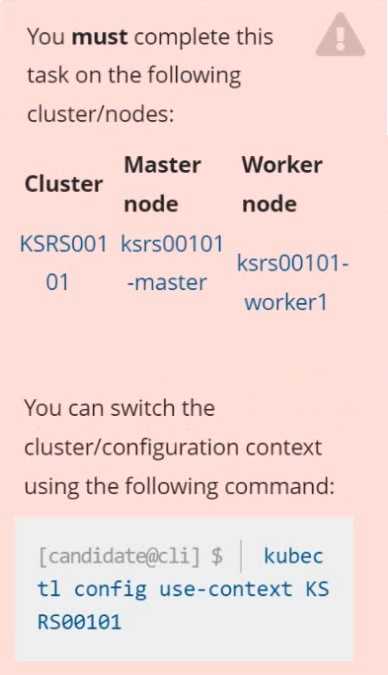
 Two tools are pre-installed on the cluster's worker node:
sysdig
 falco
 Using the tool of your choice (including any non pre-installed tool), analyze the container's behavior
for at least 30 seconds, using filters that detect newly spawning and executing processes.
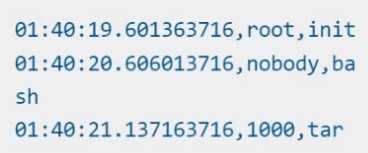
Store an incident file at /opt/KSRS00101/alerts/details, containing the detected incidents, one per
line, in the following format:
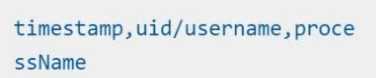 The following example shows a properly formatted incident file:
Fix all issues via configuration and restart the affected components to ensure the new setting takes effect. Fix all of the following violations that were found against the API server:- a. Ensure the --authorization-mode argument includes RBAC b. Ensure the --authorization-mode argument includes Node c. Ensure that the --profiling argument is set to false Fix all of the following violations that were found against the Kubelet:- a. Ensure the --anonymous-auth argument is set to false. b. Ensure that the --authorization-mode argument is set to Webhook. Fix all of the following violations that were found against the ETCD:- a. Ensure that the --auto-tls argument is not set to true Hint: Take the use of Tool Kube-Bench
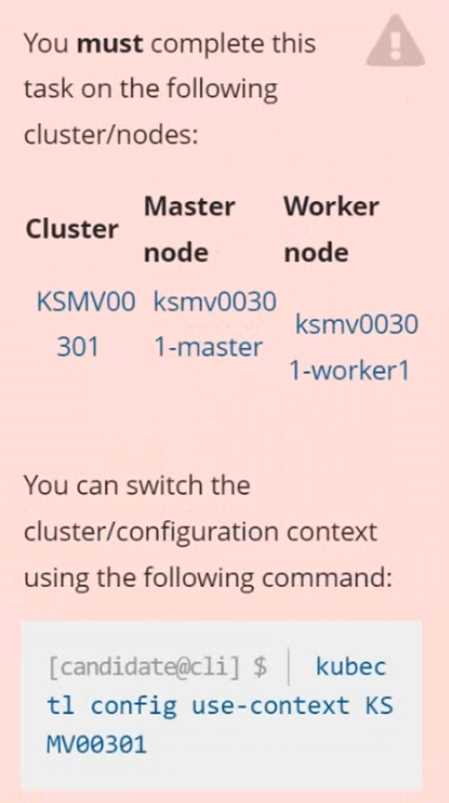 Context
This cluster uses containerd as CRI runtime.
Containerd's default runtime handler is runc. Containerd has been prepared to support an additional
runtime handler, runsc (gVisor).
Task
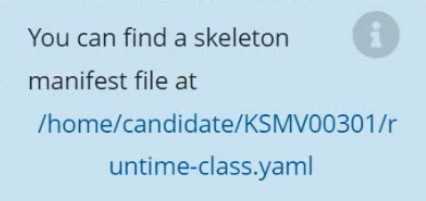
Create a RuntimeClass named sandboxed using the prepared runtime handler named runsc.
Update all Pods in the namespace server to run on gVisor.
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.