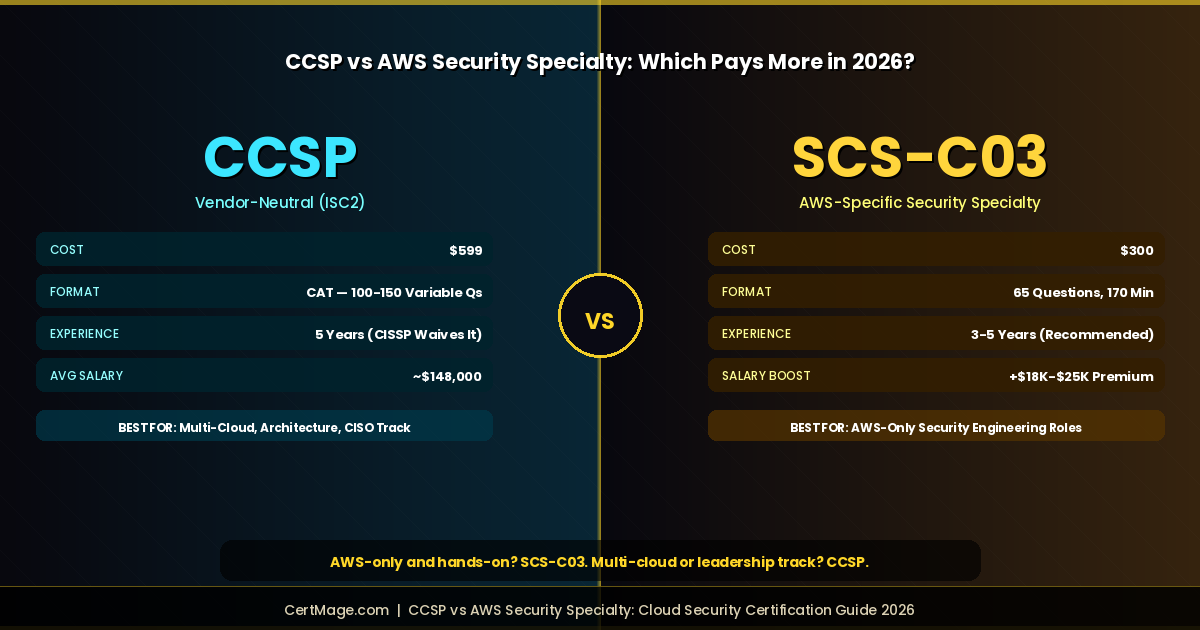
CCSP (Certified Cloud Security Professional) and AWS Certified Security – Specialty (SCS-C03) are not competing for the same job. CCSP is a vendor-neutral credential from ISC2 that validates broad cloud security knowledge applicable across AWS, Azure, and Google Cloud, commanding average salaries around $148,000 and opening paths to Cloud Security Architect, Security Consultant, and CISO roles. SCS-C03 is AWS’s deep technical credential validating hands-on security implementation specifically within AWS, with reported averages closer to $79,000 to $130,000 depending on source and role, but adding $18,000 to $25,000 in salary premium for cloud-focused roles at a $300 exam cost, one of the best ROI ratios of any certification. If your work is entirely AWS and hands-on, SCS-C03 is the more direct fit. If you want a credential that signals strategic, multi-cloud security leadership, CCSP is the stronger choice. Many cloud security professionals eventually hold both.
This guide breaks down the real differences, including how CCSP’s 2026 changes (CAT format and the upcoming August content refresh) and AWS’s 2026 SCS-C03 update affect this comparison.
CCSP vs SCS-C03: Quick Comparison
| Factor | CCSP | AWS Security Specialty (SCS-C03) |
| Issuing body | ISC2 | AWS |
| Scope | Vendor-neutral, applies across AWS, Azure, GCP | AWS-specific only |
| Domains | 6 | Multiple, including new Management & Security Governance domain |
| Exam format | CAT, 100-150 variable questions, up to 3 hours | 65 questions, 170 minutes |
| Passing score | Pass/fail via CAT algorithm | 750 out of 1000 |
| Cost | $599 | $300 |
| Experience required | 5 years (3 in security, 1 in cloud security, CISSP waives entire requirement) | 3-5 years securing cloud solutions (recommended, not mandatory) |
| Recertification | Every 3 years, 120 CPEs plus annual maintenance fee | Every 3 years, recertification exam or continuing education |
| 2026 changes | CAT format live since Oct 2025, new content outline (AI/ML security) effective August 1, 2026 | Updated to SCS-C03 with expanded emerging technology and generative AI security coverage |
| DoD recognition | Yes, DoD 8140 qualifying credential | Not a DoD 8570/8140 baseline certification |
| Typical roles | Cloud Security Architect, Security Consultant, Cloud Compliance Analyst, CISO | Cloud Security Engineer, AWS Security Specialist, DevSecOps Engineer |
CCSP: The Vendor-Neutral Case
CCSP is built around six domains covering cloud security comprehensively, without tying any of it to a specific platform’s tools or console.
CCSP’s Six Domains
| Domain | Focus |
| Cloud Concepts, Architecture and Design | Cloud computing concepts, reference architecture, secure design principles, shared responsibility model |
| Cloud Data Security | Data lifecycle, storage architectures, classification, encryption, key management, DLP |
| Cloud Platform and Infrastructure Security | Physical and logical infrastructure, virtualization security, IAM, business continuity |
| Cloud Application Security | Secure SDLC, cloud-native app security, API security |
| Cloud Security Operations | Operations management, logging, monitoring, vulnerability management, incident response |
| Legal, Risk and Compliance | Legal frameworks, privacy regulations, audits, risk management, vendor governance |
The Legal, Risk and Compliance domain is CCSP’s signature differentiator. This domain covers cloud-specific legal and regulatory considerations that vendor-provider certifications largely do not address. For Cloud Compliance Analyst roles, GRC positions, and any role where regulatory frameworks intersect with cloud architecture, this domain is directly and immediately relevant in a way no AWS-specific exam attempts to be.
What CCSP Signals to Employers
CCSP signals that you understand cloud security principles, governance, and architecture at a level that transfers across platforms. The CCSP’s vendor-neutral architecture applies across all cloud providers, making it particularly valuable for professionals working in multi-cloud environments where no single provider’s certification is sufficient. The CCSP also carries DoD 8140 recognition as a qualifying credential for advanced and mid-level cybersecurity roles, which matters for government contracting beyond its general industry value.
For the complete breakdown of what’s changing with CCSP in 2026, including the CAT format already in effect and the new exam outline arriving August 1, 2026 with AI and machine learning security content, our CCSP Exam Changes 2026 guide covers every detail.
SCS-C03: The Vendor-Specific Case
AWS Certified Security – Specialty validates a candidate’s ability to effectively demonstrate knowledge about securing AWS products and services specifically, including the ability to apply specialized data classifications and AWS data protection mechanisms, implement encryption methods using AWS mechanisms, and use AWS security services to ensure secure production environments.
SCS-C03 Target Candidate Profile
AWS recommends the equivalent of 3 to 5 years of experience securing cloud solutions, with specific knowledge of the AWS shared responsibility model, managing identity at scale, multi-account governance, managing software supply chain risks, security incident prevention and response, vulnerability management in the cloud, developing firewall rules across layers 3 through 7, incident root cause analysis, experience responding to an audit, logging and monitoring strategies, data encryption methodologies both at-rest and in-transit, and disaster recovery controls.
The SCS-C03 Update From SCS-C02
| Aspect | SCS-C02 (Previous) | SCS-C03 (Current) |
| Generative AI security | Not a dedicated focus | Expanded coverage added for emerging technologies including generative AI |
| Management & Security Governance | Introduced in SCS-C02 as a new domain covering centrally deploying and managing AWS accounts, secure deployment strategies, and compliance evaluation | Continues and expands in SCS-C03 |
| Overall depth | Established security domains across IAM, data protection, infrastructure security, detection, and incident response | Same core domains plus emerging technology focus |
SCS-C03’s strength is depth, not breadth. Candidates repeatedly work with CloudTrail, Config, GuardDuty, Security Hub, Control Tower, IAM policies, KMS encryption, and incident response tooling specific to AWS. This is the certification’s defining characteristic: it tests whether you can actually operate, configure, and troubleshoot AWS security tooling, not whether you understand security concepts in the abstract. For complete preparation covering the current SCS-C03 exam, CertMage’s SCS-C03 exam dumps cover the updated domains including the expanded emerging technology content.
CCSP vs SCS-C03: Salary Comparison
Salary data for these two certifications varies significantly across sources, which itself tells an important story.
| Source Pattern | CCSP Reported Salary | SCS-C03 Reported Salary |
| Broad averages (destcert) | $148,009 | $78,708 |
| ROI-focused analysis (redbudcyber) | Not isolated separately | Adds $18,000 to $25,000 premium on top of base role at $300 cost |
| General industry reports | $119,000 or more | Not directly compared |
Why the numbers vary so much: CCSP’s reported salaries often reflect the senior, architect-level, and leadership roles it feeds into (Cloud Security Architect, CISO, Security Consultant), which carry inherently higher compensation. SCS-C03’s reported salaries often reflect it as an add-on credential to an existing AWS engineering role (Cloud Security Engineer, DevSecOps Engineer) rather than the primary qualification for a senior title. The honest interpretation is not that CCSP “pays more” in some absolute sense, but that CCSP is more frequently associated with senior and leadership titles, while SCS-C03 is more frequently associated with a salary premium added to an existing technical role.
The premium framing matters. At $300 cost, SCS-C03 adding $18,000 to $25,000 to a cloud-focused role represents one of the strongest cost-to-salary-increase ratios of any cybersecurity certification. CCSP at $599 cost commands a higher absolute salary association, but that figure reflects the seniority of roles it’s associated with as much as the certification’s direct salary impact.
CCSP vs SCS-C03: Which Is Harder?
| Factor | CCSP | SCS-C03 |
| Knowledge type | Conceptual, governance, architecture, broad principles | Hands-on, platform-specific, operational depth |
| Exam format challenge | CAT format means early questions shape difficulty trajectory; 100-150 variable questions | Fixed 65 questions, but each requires deep AWS-specific scenario knowledge |
| Where candidates struggle | Legal, Risk and Compliance domain for candidates without GRC background; broad scope across 6 domains | Breadth and depth of AWS service-specific knowledge; considered challenging even for experienced professionals |
| Best background for success | Security professionals with multi-cloud or governance exposure | AWS-focused security engineers with daily hands-on AWS security tooling experience |
CCSP is less about tricky technical questions and more about how well you understand the cloud security ecosystem conceptually. SCS-C03 is considered demanding due to its breadth and depth of AWS-specific content, and candidates without daily AWS security operations experience often underestimate how deep the service-specific knowledge requirements go.
CCSP vs SCS-C03: Career Path Comparison
| Career Direction | Better Fit |
| Multi-cloud security architecture | CCSP |
| AWS-only security engineering | SCS-C03 |
| Governance, risk, and compliance roles | CCSP |
| DevSecOps within AWS environments | SCS-C03 |
| Security leadership (CISO track) | CCSP |
| Hands-on incident response on AWS | SCS-C03 |
| Government and DoD contracting | CCSP (DoD 8140 recognized) |
| Cloud Security Consultant (multi-client) | CCSP |
| Senior AWS-specific technical roles | SCS-C03, often paired with Solutions Architect Professional |
Should You Get Both?
For professionals planning a long-term cloud security career, particularly in organizations with significant AWS investment but multi-cloud exposure, holding both certifications is increasingly common and increasingly valuable.
| Sequence | Why It Works |
| SCS-C03 first, then CCSP | Establishes hands-on AWS credibility early in career, then adds strategic and multi-cloud framing as you move toward architecture or leadership roles |
| CCSP first, then SCS-C03 | Establishes broad governance and architecture framing first (useful if coming from a CISSP or general security background), then adds AWS-specific technical depth |
AWS Security first for impact, CCSP second for leadership is one common framing: get the hands-on AWS credential early to prove technical competence, then add CCSP as your career moves toward architecture, consulting, or leadership where multi-cloud and governance framing matters more than single-platform depth.
The CISSP connection matters here too. If you already hold CISSP, it satisfies the entire CCSP experience requirement, making CCSP a faster add-on. For professionals who hold CISSP and are AWS-focused, the practical sequence often becomes CISSP, then SCS-C03 for AWS depth, then CCSP to formalize multi-cloud governance credibility, since CISSP has already cleared CCSP’s experience bar.
CCSP vs SCS-C03: Cost Comparison
| Cost Item | CCSP | SCS-C03 |
| Exam fee | $599 | $300 |
| Annual maintenance fee | Yes (ISC2 AMF) | No separate AMF, but recertification required every 3 years |
| Recertification | 120 CPE credits over 3 years | Recertification exam or continuing education every 3 years |
| Study materials | $100-$300 typical | $50-$200 typical |
SCS-C03 at $300 is roughly half the cost of CCSP at $599, with no separate annual maintenance fee structure, making it the lower-cost entry point of the two. CCSP’s higher cost reflects both ISC2’s general pricing and the broader scope and ongoing professional membership structure that comes with ISC2 certifications.
FAQS
What is the difference between CCSP and AWS Security Specialty?
CCSP is a vendor-neutral certification from ISC2 covering cloud security principles, architecture, governance, and compliance applicable across AWS, Azure, and Google Cloud. AWS Security Specialty (SCS-C03) is AWS’s vendor-specific certification validating hands-on security implementation skills specifically within the AWS ecosystem.
Which pays more, CCSP or AWS Security Specialty?
Reported figures vary widely by source. CCSP is often associated with average salaries around $148,000, reflecting the senior architecture and leadership roles it feeds into. SCS-C03 is often reported lower in absolute terms (around $79,000 in some sources) but adds a $18,000 to $25,000 premium to cloud-focused roles at a $300 cost, representing strong ROI. The difference largely reflects role seniority rather than the certifications themselves.
Which is harder, CCSP or AWS Security Specialty?
Both are considered challenging but in different ways. CCSP’s difficulty comes from breadth across 6 domains and its CAT exam format with 100-150 variable questions. SCS-C03’s difficulty comes from the depth of AWS-specific service knowledge required, which is considered demanding even for experienced professionals. CCSP rewards conceptual and governance understanding; SCS-C03 rewards hands-on AWS operational experience.
Should I get CCSP or AWS Security Specialty first?
If your work is currently AWS-focused and hands-on, SCS-C03 is the more immediate fit and costs less ($300 vs $599). If you are aiming toward multi-cloud architecture, consulting, or security leadership, CCSP provides the broader framing employers look for in those roles. Many professionals get SCS-C03 first for technical credibility, then CCSP as their career moves toward leadership.
Does CCSP cover AWS specifically?
No. CCSP is explicitly vendor-neutral and does not test AWS-specific tools, console operations, or service configurations. It covers cloud security concepts, architecture, and governance that apply across AWS, Azure, Google Cloud, and other platforms.
Is CCSP or AWS Security Specialty recognized by the DoD?
CCSP is recognized under the DoD 8140 framework as a qualifying credential for advanced and mid-level cybersecurity roles. AWS Security Specialty (SCS-C03) is not part of the DoD 8570/8140 baseline certification list.
What changed with AWS Security Specialty in 2026?
AWS updated the exam from SCS-C02 to SCS-C03, expanding coverage of emerging technologies with a dedicated focus on generative AI security, building on SCS-C02’s introduction of the Management & Security Governance domain covering centralized AWS account management and compliance evaluation.
What changed with CCSP in 2026?
CCSP transitioned to Computerized Adaptive Testing (CAT) format effective October 1, 2025, using 100-150 variable questions in up to 3 hours. A new exam outline takes effect August 1, 2026, adding AI and machine learning security content including OWASP LLM Top 10 coverage, while keeping the same six-domain structure.
Can CCSP substitute for AWS Security Specialty experience requirements?
No, they are independent certifications from different organizations with separate experience requirements. However, if you hold CISSP, it satisfies the entire CCSP experience requirement, which can make pursuing CCSP faster for CISSP holders who also want to add SCS-C03 for AWS-specific depth.
Is it worth getting both CCSP and AWS Security Specialty?
For professionals in organizations with significant AWS investment and multi-cloud exposure, or those planning a path toward cloud security architecture or leadership, holding both is increasingly valuable. SCS-C03 establishes AWS-specific technical credibility at lower cost ($300), while CCSP adds vendor-neutral governance and multi-cloud framing valued in senior and consulting roles ($599).