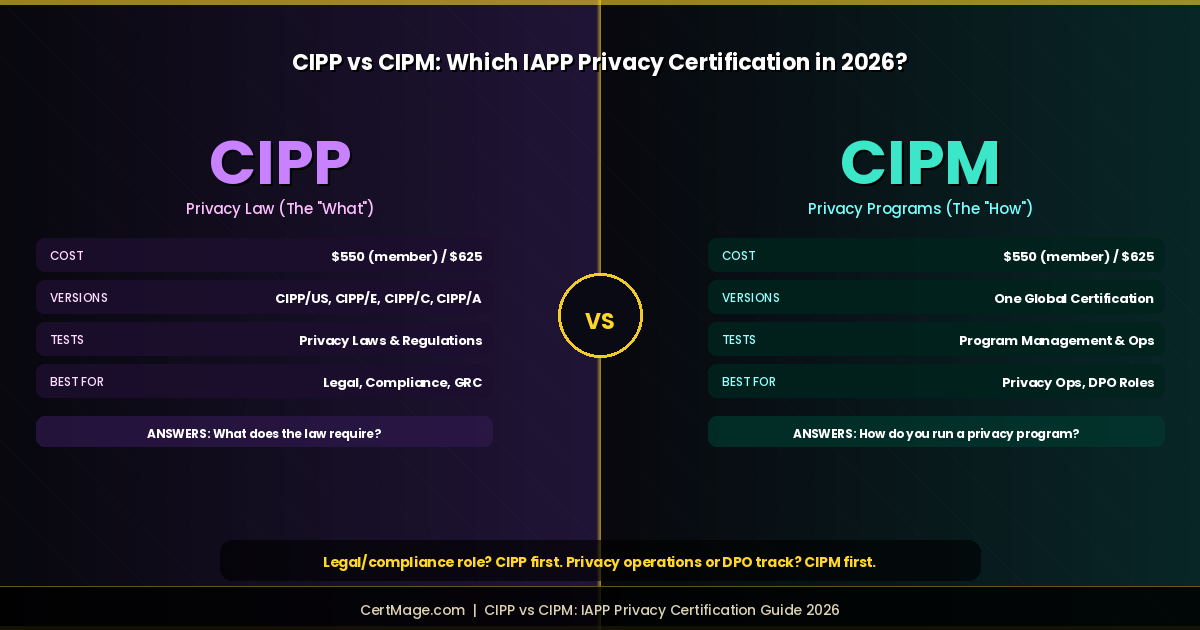
CIPP vs CIPM comes down to law versus operations. CIPP (Certified Information Privacy Professional) validates that you understand privacy laws and regulations, the “what” of privacy: what GDPR requires, what CCPA covers, what HIPAA mandates. CIPM (Certified Information Privacy Manager) validates that you can build and run a privacy program, the “how” of privacy: how to implement a data inventory, how to manage data subject access requests, how to operationalize compliance day to day. Both are issued by the IAPP (International Association of Privacy Professionals), the leading global body for privacy credentials. If your role involves interpreting privacy law, compliance assessments, or legal risk, start with CIPP. If your role involves running privacy operations, managing a privacy team, or implementing privacy programs, start with CIPM. Many privacy professionals eventually hold both, and the combination is one of the strongest signals in the privacy field.
This guide breaks down exactly what each certification tests, who each is for, and how to plan your path between them.
CIPP vs CIPM: Quick Comparison
| Factor | CIPP | CIPM |
| Full name | Certified Information Privacy Professional | Certified Information Privacy Manager |
| Core question answered | What does the law require? | How do you run a privacy program? |
| Focus | Privacy laws, regulations, and jurisdictional requirements | Privacy program operations, governance, and lifecycle management |
| Available specializations | CIPP/US, CIPP/E, CIPP/C, CIPP/A | One version, globally applicable |
| Best suited for | Legal, compliance, GRC, privacy counsel | Privacy operations managers, DPOs, program leads |
| Prerequisite | None | None |
| Exam format | Multiple choice | Multiple choice |
| Issuing body | IAPP | IAPP |
| Membership required to maintain | Yes | Yes |
| Typical pairing | Often taken before CIPM for legal foundation | Often taken after CIPP for operational application |
What CIPP Covers
CIPP is not a single exam. It is a family of jurisdiction-specific certifications, each focused on the privacy laws of a particular region.
The CIPP Family
| Certification | Jurisdiction Focus | Best For |
| CIPP/US | United States federal and state privacy laws | Privacy professionals working with US data, US-based legal and compliance roles |
| CIPP/E | European Union data protection law, primarily GDPR | Privacy professionals working with EU data, GDPR compliance roles |
| CIPP/C | Canadian federal and provincial privacy laws | Privacy professionals working with Canadian data |
| CIPP/A | Asia-Pacific privacy laws and frameworks | Privacy professionals working across APAC jurisdictions |
CIPP/US and CIPP/E are by far the most commonly pursued. CIPP/US covers the patchwork of US federal sectoral laws (HIPAA, GLBA, COPPA, FCRA) alongside the growing landscape of state privacy laws (CCPA/CPRA, and the wave of comprehensive state privacy laws that followed). CIPP/E covers the GDPR in depth, along with the broader EU and EEA data protection framework.
What CIPP Actually Tests
CIPP exams test your ability to interpret and apply privacy law to real scenarios. Expect questions structured around: identifying which law applies to a given scenario, determining what a specific regulation requires an organization to do, recognizing the rights a regulation grants to individuals, and identifying enforcement mechanisms and penalties for non-compliance.
This is fundamentally legal and regulatory knowledge. CIPP does not test how to build a privacy program, how to write a data inventory, or how to respond operationally to a data breach. It tests whether you know what the law says.
Who CIPP Is For
CIPP is the right starting point if your role involves: advising on privacy law compliance, conducting privacy impact assessments from a legal risk perspective, working in legal, compliance, or GRC functions, or supporting a Data Protection Officer in interpreting regulatory requirements. Privacy attorneys, compliance analysts, and legal counsel most directly benefit from CIPP’s regulatory focus. For complete preparation covering US privacy law, CertMage’s CIPP-US exam dumps cover the current exam blueprint. For GDPR and EU-focused preparation, CertMage’s CIPP-E exam dumps cover the European data protection framework in depth.
What CIPM Covers
CIPM is a single, globally applicable certification focused on privacy program management rather than any specific jurisdiction’s laws.
CIPM’s Core Domains
| Area | What It Covers |
| Privacy program governance | Establishing a privacy program framework, roles, responsibilities, and structure |
| Privacy program operational lifecycle | Assessing, protecting, sustaining, and responding within an ongoing privacy program |
| Data inventory and mapping | Identifying what personal data an organization holds, where it lives, and how it flows |
| Privacy by design | Embedding privacy considerations into products, processes, and systems from the start |
| Data subject rights management | Operationalizing how an organization responds to access, deletion, and correction requests |
| Incident response and breach management | Building and executing the operational response to a privacy incident |
| Vendor and third-party risk management | Assessing and managing privacy risk introduced by vendors and partners |
| Training and awareness | Building organizational privacy culture and training programs |
What CIPM Actually Tests
CIPM exams test your ability to design, build, and operate a privacy program. Expect questions structured around: how to structure a privacy program for an organization of a given size and risk profile, what steps to take when implementing a data inventory, how to prioritize and respond to a privacy incident operationally, and how to measure and report on privacy program effectiveness.
This is operational and managerial knowledge. CIPM assumes you understand that privacy laws exist and create obligations, but it does not test the specific legal content of any particular jurisdiction’s regulations in depth.
Who CIPM Is For
CIPM is the right starting point if your role involves: building or running a privacy program from the ground up, managing a privacy team or function, serving as or supporting a Data Protection Officer operationally, or implementing the practical mechanisms (data inventories, DSAR processes, incident response plans) that turn legal requirements into working systems. For complete preparation, CertMage’s CIPM exam dumps cover all aspects of privacy program management tested on the current exam.
For the complete cost breakdown of CIPM including exam fees, membership dues, and budget scenarios, our CIPM Certification Cost guide covers every fee in detail. For India-specific salary data for CIPM holders, our CIPM Salary in India guide covers city-by-city compensation.
CIPP vs CIPM: The Practical Difference With an Example
Consider a scenario: a company experiences a data breach involving customer personal information.
CIPP knowledge answers: Which breach notification laws apply based on where the affected individuals live? What is the legally required notification timeline under GDPR versus under US state breach notification laws? What regulatory body must be notified, and what penalties could apply for non-compliance?
CIPM knowledge answers: Does the organization have an incident response plan that covers this scenario? Who internally needs to be notified, and in what order? How does the organization identify which systems and data were affected? What is the operational process for drafting and sending breach notifications once the legal requirements are known?
The two are complementary, not redundant. CIPP tells you what the law requires. CIPM tells you how an organization actually executes on that requirement. An organization needs both kinds of knowledge represented, whether in one person or across a team.
CIPP vs CIPM: Which Should You Take First?
| Your Situation | Recommended First Certification |
| You work in legal, compliance, or GRC | CIPP (choose CIPP/US, CIPP/E, or others based on your jurisdiction focus) |
| You work in or are moving into privacy operations or program management | CIPM |
| You are a Data Protection Officer or aspiring DPO | CIPP first for legal grounding, then CIPM for operational depth (many DPO roles expect both) |
| You are new to privacy entirely, coming from a technical background | CIPM may feel more familiar initially (process and systems-oriented), but CIPP builds the legal vocabulary that makes CIPM’s “why” make sense |
| You are new to privacy entirely, coming from a legal background | CIPP first, building on existing legal analysis skills |
| Your organization operates primarily in one jurisdiction (e.g., US-only) | CIPP/US first, then CIPM |
| Your organization operates across multiple jurisdictions | CIPP/E often first (GDPR’s influence shapes global privacy practice broadly), then CIPM, with CIPP/US added depending on US operations |
The honest reality: there is no universally correct order. CIPP and CIPM validate different kinds of knowledge that support each other but do not depend on each other. The right starting point is determined by what your current role demands most immediately, not by an abstract “easier first” or “harder first” logic.
CIPP vs CIPM: Career Paths and Roles
| Certification | Common Job Titles |
| CIPP/US | Privacy Counsel, Compliance Analyst (Privacy), Privacy Risk Analyst, GRC Analyst |
| CIPP/E | EU Privacy Specialist, GDPR Compliance Manager, Data Protection Analyst |
| CIPM | Privacy Program Manager, Data Protection Officer, Director of Privacy, Privacy Operations Manager |
| CIPP plus CIPM | Senior Privacy Counsel, Chief Privacy Officer, Head of Data Protection |
The combination of CIPP and CIPM is particularly valued for Data Protection Officer roles and senior privacy leadership, where both legal interpretation and operational program management are core responsibilities of the same position.
CIPP vs CIPM: Cost Comparison
| Cost Item | CIPP (per jurisdiction) | CIPM |
| Exam fee | $550 (member) / $625 (non-member) | $550 (member) / $625 (non-member) |
| IAPP membership (if not already a member) | $75 to $95 per year | $75 to $95 per year |
| Recertification | Every 2 years, 20 CPE credits | Every 2 years, 20 CPE credits |
Both certifications are priced identically by IAPP. The cost difference comes from how many you pursue: a CIPP/US plus CIPM combination costs roughly the same as CIPP/E plus CIPM, but pursuing multiple CIPP jurisdictions (for example CIPP/US and CIPP/E together) roughly doubles the CIPP-specific investment. For the complete CIPM cost breakdown including all budget scenarios, our CIPM Certification Cost guide covers every fee and strategy to reduce cost.
FAQS
What is the difference between CIPP and CIPM?
CIPP (Certified Information Privacy Professional) validates knowledge of privacy laws and regulations, what the law requires in a given jurisdiction. CIPM (Certified Information Privacy Manager) validates the ability to build and operate a privacy program, how an organization implements and manages compliance day to day. CIPP is jurisdiction-specific (CIPP/US, CIPP/E, CIPP/C, CIPP/A). CIPM is a single, globally applicable certification.
Should I get CIPP or CIPM first?
It depends on your role. If you work in legal, compliance, or GRC and need to interpret privacy law, start with CIPP for your relevant jurisdiction. If you work in or are moving toward privacy operations, program management, or a DPO role, start with CIPM. Many professionals eventually hold both, and there is no universally correct order.
Which CIPP should I take, CIPP/US or CIPP/E?
Choose based on the jurisdiction most relevant to your work. CIPP/US covers US federal sectoral laws (HIPAA, GLBA, COPPA) and the growing landscape of state privacy laws (CCPA/CPRA and similar). CIPP/E covers GDPR and the broader EU data protection framework. If your organization operates in both regions, both certifications have value, with CIPP/E often considered first given GDPR’s broad influence on global privacy practice.
Can CIPM be taken without CIPP?
Yes. Neither CIPP nor CIPM has a formal prerequisite. They can be pursued in any order or independently, based on what your role requires.
How much do CIPP and CIPM cost?
Both are priced identically by IAPP: $550 for IAPP members or $625 for non-members per exam. IAPP membership costs $75 to $95 per year. Pursuing multiple CIPP jurisdictions (for example both CIPP/US and CIPP/E) roughly doubles the CIPP-specific cost, while CIPM remains a single exam regardless of jurisdiction.
Is CIPM harder than CIPP?
Difficulty is subjective and depends on your background. Candidates with legal backgrounds often find CIPP’s content more familiar (interpreting statutes and regulations), while candidates with operations or management backgrounds often find CIPM’s content more familiar (program design, process implementation). Neither is definitively harder; they test different kinds of knowledge.
Do CIPP and CIPM expire?
Yes. Both require recertification every 2 years through 20 CPE (Continuing Privacy Education) credits per certification held, plus maintaining active IAPP membership.
What roles benefit most from holding both CIPP and CIPM?
Data Protection Officer, Chief Privacy Officer, Senior Privacy Counsel, and Head of Data Protection roles particularly value both, since these positions typically require both legal interpretation (CIPP) and operational program management (CIPM) within the same role.
Is CIPP or CIPM more recognized by employers?
Both are widely recognized as IAPP credentials, the leading global privacy certification body. Recognition often depends on the specific role: legal and compliance job postings more frequently reference CIPP (often a specific jurisdiction), while privacy operations and DPO job postings more frequently reference CIPM, sometimes alongside CIPP.
Which IAPP certification should a Data Protection Officer have?
Many DPO roles list CIPP and CIPM together, or treat either as acceptable with the other preferred. Since the DPO role spans both legal interpretation and operational program management, holding both certifications is increasingly the standard expectation for senior DPO positions.