
GIAC certification practice
Free GPEN Practice Test
10 free GPEN exam-style questions for GIAC Penetration Tester Certification (GPEN), with answers, explanations and source references.
Full set: 385 questionsThe GPEN exam leads to the GIAC Penetration Tester Certification (GPEN), for people who plan and carry out penetration tests. The version released on or after July 12th, 2025 has 82 questions in 3 hours, needs a minimum score of 73%, and is proctored remotely through ProctorU or onsite through Pearson VUE.
The exam covers a broad range of objectives. The objectives run from penetration test planning, reconnaissance and scanning through exploitation with Metasploit, command and control, and escalation. A large share covers credentials: password formats and hashes, attacking hashes, Kerberos attacks, and domain escalation and persistence. The Azure objectives add cloud and AD integration material, so study it alongside the on-premises topics. Because the exam includes CyberLive hands-on lab challenges, reading real tool output matters as much as knowing definitions.
Work through the free practice questions one at a time and check each answer before moving on. Read every explanation, including for questions you got right, since it often shows why a related technique would fail. Note which objectives cause repeated mistakes, such as Kerberos or hash attacks, and revisit them before your next set.
About the exam
GPEN exam at a glance
Key facts for the GIAC Penetration Tester Certification (GPEN) exam, taken from the official exam page.
| Exam code | Exam version released on or after July 12th, 2025 |
|---|---|
| Number of questions | 82 |
| Time allowed | 180 minutes |
| Passing score | 73% |
| Question types | Includes CyberLive hands-on, performance-based lab challenges (virtual machines, real tools) |
| Delivery | Web-based, proctored; remote proctoring through ProctorU or onsite proctoring through Pearson VUE |
Source: official GPEN exam page. Verified . Prices and policies can change, so confirm with the provider before booking.
Exam objectives
What the GPEN exam covers
The GPEN exam is organized into 16 official domains. Weight shows the share of the exam each domain represents, so spend your study time in proportion.
- Advanced Password Attacks
- Attacking Password Hashes
- Azure Applications and Attack Strategies
- Azure Overview, Attacks, and AD Integration
- Command and Control (C2)
- Domain Escalation and Persistence Attacks
- Escalation and Exploitation
- Exploitation Fundamentals
- Kerberos Attacks
- Metasploit
- Password Attacks
- Password Formats and Hashes
- Penetration Test Planning
- Reconnaissance
- Scanning and Host Discovery
- Vulnerability Scanning
Domains and weights from the official GPEN exam outline.
Quick answers
GPEN exam FAQ
How many questions are on the GPEN exam?
The GPEN exam has 82 questions and gives you 180 minutes to finish. Question types include includes CyberLive hands-on, performance-based lab challenges (virtual machines, real tools).
What is the passing score for GPEN?
You need 73% to pass the GIAC Penetration Tester Certification (GPEN) exam.
Study resources
GPEN study guides and comparisons
Go deeper than the practice questions: certification comparisons, study plans, and career context for GPEN.
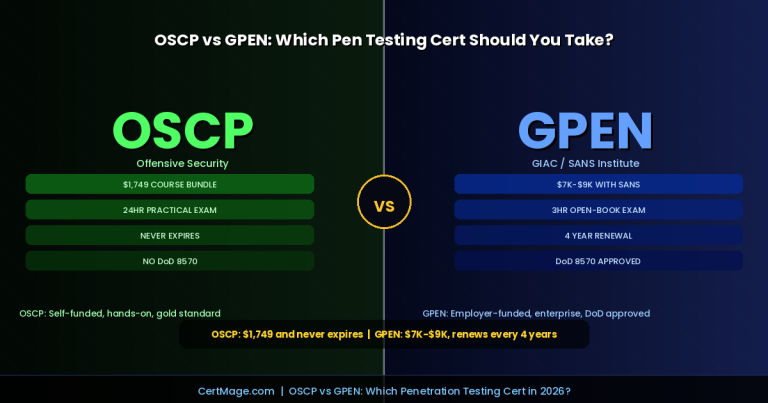 IT Certification Comparisons · 14 min read
OSCP vs GPEN: Which Penetration Testing Certification Should You Take in 2026?
Read the guide
 Cybersecurity Certifications · 18 min read
Best Cybersecurity Certifications 2026: 14 Credentials Ranked by Salary, ROI, and Career Path
Read the guide
 Cybersecurity Certifications · 17 min read
Is Ethical Hacking A Good Career? Revealing Their Essence in Hacking Department
Read the guide
Source context
How this practice set is maintained
Maintained by the CertMage content team, this page loads questions from the exam dataset connected to its preparation resource. When an answer includes a supporting reference, it is shown with that answer so you can review the underlying vendor documentation.
Certification objectives, interfaces, and vendor services can change. Verify important details against the provider's current exam guide and documentation before your exam.
Reviewed by Alexandra Stone CISSP, CISM, CISA, Security+, CEH