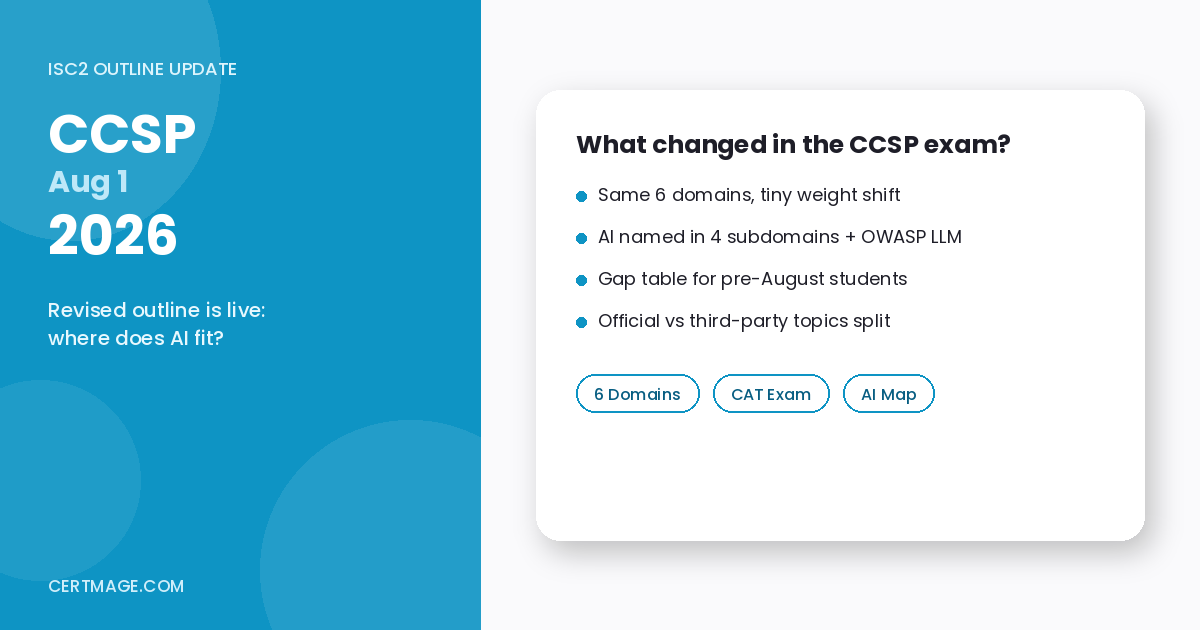
TL;DR: ISC2’s revised Certified Cloud Security Professional (CCSP) exam outline is dated August 1, 2026, and it keeps the same six domains. The weights barely moved. Two third-party breakdowns show only Cloud Application Security slipping from 17% to 16% and Cloud Security Operations rising from 16% to 17%. The real change is content. ISC2’s outline now builds AI and machine learning into four subdomains (1.2, 1.6, 2.9 and 5.6) and names the OWASP Top 10 for LLM Applications in subdomain 4.1. ISC2 does not publish domain weights on the outline page we could read, and several third-party sites list extra topics (zero trust, SBOMs, EU AI Act, NIS2, DORA) that do not appear as named subdomains, so this guide separates what ISC2’s page shows from what other sites report. If you studied before August, the gap is small in percentages but real in content.
CCSP candidates tend to ask one question after an outline change: “Do I need to start over?” For most people the answer is no. You need to add a layer of AI and application security topics on top of what you already know. This guide shows exactly where.
Quick Facts
| Item | What the sources say |
| Exam | ISC2 Certified Cloud Security Professional (CCSP) |
| Revised outline date | August 1, 2026 (shown on ISC2’s outline page and announced by ISC2 in June 2026) |
| Domains | 6, unchanged in name |
| Required work experience | 5 years (stated on ISC2’s CCSP page) |
| Reported weights (new outline) | 17%, 20%, 17%, 16%, 17%, 13% for domains 1 to 6 |
| Reported weights (old outline) | 17%, 20%, 17%, 17%, 16%, 13% for domains 1 to 6 |
| Format | Computerized adaptive testing (CAT), reported as 100 to 150 questions in up to 3 hours |
| Passing score | 700 out of 1,000 (reported) |
| Reported fee | $599 per attempt in the Americas |
| Reported annual maintenance fee | $125 per year |
| Reported continuing education | 90 credits per 3 year cycle, 60 of them cloud specific |
Items marked “reported” come from third-party sources. ISC2’s CCSP page and outline page, as we could read them, did not list the format, fee or weights.
What Changed at a Glance
The weights
| Domain | Old outline | New outline | Change |
| 1. Cloud Concepts, Architecture and Design | 17% | 17% | None |
| 2. Cloud Data Security | 20% | 20% | None |
| 3. Cloud Platform and Infrastructure Security | 17% | 17% | None |
| 4. Cloud Application Security | 17% | 16% | Down 1 point |
| 5. Cloud Security Operations | 16% | 17% | Up 1 point |
| 6. Legal, Risk and Compliance | 13% | 13% | None |
These figures come from two third-party sources that agree with each other, and a third site lists the older set. Neither ISC2 page we read showed the weights, so treat them as reported until you check ISC2’s materials.
The lesson is that a one-point shift means almost nothing for study planning. What matters is what sits inside each domain.
The date ladder
| Date | Event | Source |
| August 1, 2024 | Exam reduced from 150 questions in four hours to 125 questions in three hours | Reported by one third-party source |
| October 1, 2025 | English exam moved to computerized adaptive testing | Reported by two sources, including CertMage’s own earlier post |
| June 2026 | ISC2 announced the revised outline | ISC2 article, “ISC2 Refreshes CCSP Exam” |
| August 1, 2026 | Revised outline takes effect | ISC2’s outline page and announcement |
ISC2’s June announcement cites its Cybersecurity Workforce Study, which says cloud security is the second most in-demand skill, behind only AI. That context explains why the update leans so heavily on AI.
The AI Map: Where ISC2 Puts AI in the Outline
This is the most useful table in the post. We read ISC2’s outline page and listed every place it names AI, ML or LLM topics in an enumerated subdomain.
| Subdomain | What the outline says | Domain |
| 1.2 Cloud reference architecture | Includes the impact of AI, ML and related technologies | 1. Cloud Concepts, Architecture and Design |
| 1.6 AI/ML | Threat detection, SOAR, ethics and regulatory requirements | 1. Cloud Concepts, Architecture and Design |
| 2.9 AI/ML data protection | Dataset and model privacy and security | 2. Cloud Data Security |
| 4.1 Application security training | OWASP Top 10, ASVS, OWASP API Top 10 and the OWASP Top 10 for LLM Applications | 4. Cloud Application Security |
| 5.6 Security operations | SOC, SIEM, incident response, vulnerability assessment and penetration testing, including AI-based monitoring | 5. Cloud Security Operations |
Three details are worth noting.
- AI and ML are named in four subdomains (1.2, 1.6, 2.9 and 5.6), and subdomain 4.1 adds the LLM list. Domains 3 and 6 have no enumerated AI subdomain.
- LLM appears only once, through the OWASP Top 10 for LLM Applications in subdomain 4.1.
- The word “agentic” does not appear in the enumerated subdomains we read.
ISC2’s page also contains narrative sections about AI in each domain, mentioning ideas such as homomorphic encryption, differential privacy, prompt injection, model drift and the EU AI Act. None of those terms appear in the enumerated subdomains. A careful reader should treat them as descriptive commentary and not as guaranteed test objectives unless ISC2 says otherwise. Still, they are worth a short read, because a topic described in the outline’s narrative can show up in scenario wording.
Domain by Domain: What ISC2’s Outline Lists
Domain 1: Cloud Concepts, Architecture and Design (reported 17%)
| Subdomain | Topic | What changed |
| 1.1 | Cloud computing concepts | Core |
| 1.2 | Cloud reference architecture | Now includes AI and ML impact |
| 1.3 | Cloud security concepts | Core |
| 1.4 | Secure cloud design principles | Includes DevOps security |
| 1.5 | Evaluating cloud service providers | Core |
| 1.6 | AI/ML | Threat detection, SOAR, ethics, regulatory requirements |
Domain 2: Cloud Data Security (reported 20%)
| Subdomain | Topic | What changed |
| 2.1 | Data concepts and flows | Core |
| 2.2 | Storage architectures and threats | Core |
| 2.3 | Encryption, hashing, obfuscation, tokenization, DLP, key management | Core |
| 2.4 | Data discovery | Core |
| 2.5 | Classification | Core |
| 2.6 | Information Rights Management | Core |
| 2.7 | Retention, deletion, archiving, legal hold | Core |
| 2.8 | Auditability, traceability, accountability | Core |
| 2.9 | AI/ML data protection | Dataset and model privacy and security |
Domain 2 remains the heaviest domain at a reported 20%, and subdomain 2.9 is the AI addition.
Domain 3: Cloud Platform and Infrastructure Security (reported 17%)
| Subdomain | Topic |
| 3.1 | Infrastructure and platform components |
| 3.2 | Secure data center design |
| 3.3 | Cloud risk analysis |
| 3.4 | Security controls |
| 3.5 | Business continuity and disaster recovery |
Domain 3 has no named AI subdomain. One third-party source reports clearer resilience requirements and “risk treatment” wording here. We could not match that to ISC2’s page, so treat it as reported.
Domain 4: Cloud Application Security (reported 16%
| Subdomain | Topic | What changed |
| 4.1 | Application security training | Names OWASP Top 10, ASVS, OWASP API Top 10 and OWASP Top 10 for LLM Applications |
| 4.2 | Secure SDLC | Core |
| 4.3 | Applying the SDLC | Threat modeling, secure coding, configuration management |
| 4.4 | Software assurance and testing | SAST, DAST, SCA, IAST |
| 4.5 | Verified secure software and supply chain | Core |
| 4.6 | Cloud application architecture | Core |
| 4.7 | Identity and access management | Core |
This domain dropped one reported point, and subdomain 4.1 now names the LLM application risk list. If your study notes stop at the classic OWASP Top 10, add the API and LLM lists.
Domain 5: Cloud Security Operations (reported 17%)
| Subdomain | Topic | What changed |
| 5.1 | Building infrastructure | Core |
| 5.2 | Operating infrastructure | Core |
| 5.3 | Operational controls and standards | ITIL, ISO, NIST and others |
| 5.4 | Digital forensics | Core |
| 5.5 | Stakeholder communication | Core |
| 5.6 | Security operations | SOC, SIEM, incident response, vulnerability assessment, penetration testing, now including AI-based monitoring |
Domain 6: Legal, Risk and Compliance (reported 13%)
| Subdomain | Topic |
| 6.1 | Legal requirements and eDiscovery |
| 6.2 | Privacy |
| 6.3 | Audit processes |
| 6.4 | Enterprise risk management |
| 6.5 | Outsourcing and contract design |
Domain 6 is the smallest domain and has no named AI subdomain, though the narrative text refers to AI regulation.
Official Outline vs Third-Party Lists: Where They Differ
Several sites list more topics than ISC2’s enumerated subdomains show. Here is how to read the difference.
| Topic reported by third parties | Where we found it in ISC2’s outline | Verdict |
| AI and ML objectives in Domain 1 | Yes, subdomains 1.2 and 1.6 | Confirmed |
| AI/ML dataset and model protection in Domain 2 | Yes, subdomain 2.9 | Confirmed |
| OWASP API and LLM risks in Domain 4 | Yes, subdomain 4.1 | Confirmed |
| SAST, DAST, SCA | Yes, subdomain 4.4 | Confirmed |
| AI-based monitoring in Domain 5 | Yes, subdomain 5.6 | Confirmed |
| Zero trust as a distinct topic (ZTNA, micro-segmentation, SASE, CISA maturity model) | Not an enumerated subdomain | Reported only |
| SBOMs and build pipeline security | Software supply chain appears in 4.5, but SBOM is not named | Partly reported |
| Containers, Kubernetes and serverless security | Not named in the subdomain list we read | Reported only |
| EU AI Act, NIS2, DORA, NIST AI RMF | Not named in the enumerated subdomains. The narrative mentions the EU AI Act | Reported or narrative only |
| Data stewards, risk and control self-assessments, more privacy laws in Domain 6 | Not named in the enumerated subdomains | Reported only |
The safe approach: study every confirmed item, then treat the “reported only” items as extras worth a quick review. Cloud security candidates will probably meet most of them at work anyway.
Format: What We Know About the CAT Exam
| Feature | Report |
| Testing method | Computerized adaptive testing |
| Length | 100 to 150 questions |
| Typical length | One source says the exam typically contains 125 questions |
| Time limit | Up to 3 hours |
| Unscored items | One source says the minimum-length exam includes 25 unscored pretest items |
| Review | Questions are presented one at a time, and submitted answers cannot be changed or revisited |
| Early finish | The exam ends once the system reaches the required confidence after the minimum length |
| Passing score | 700 out of 1,000 |
| Languages | One source lists English, Chinese, Japanese and German |
An adaptive exam rewards a calm pace. You cannot skip a question and return, so decide, answer and move on. The format has been in place since October 2025, so it is not new in this update.
ISC2’s own pages, as we could read them, did not state the question count, time or passing score. These details come from third-party sources, so check ISC2’s exam policy page before you book.
Cost, Experience and Maintenance
| Item | Report | Source type |
| Exam fee | $599 per attempt (Americas), full fee again for retakes | Third party |
| Required work experience | 5 years | ISC2’s CCSP page |
| Experience breakdown | Five years cumulative full-time IT experience, including three in information security and one in one or more CCSP domains | Third party |
| Degree waiver | A relevant degree can waive up to one year | Third party |
| CCSK | Can substitute for one year, with only one year waived in total | Third party |
| Active CISSP | Waives the entire CCSP experience requirement | Third party |
| Without the experience | You can pass and become an Associate of ISC2, with six years to meet the requirement | Third party |
| Annual maintenance fee | $125 per year | Third party |
| Continuing education | 90 credits per 3 year cycle, 60 cloud specific | Third party |
The experience breakdown and waivers are widely repeated, but ISC2’s page, as we read it, showed only “5 years.” Confirm the waiver details on ISC2’s site before relying on them.
Should You Take CCSP? A Decision Table
| Your situation | Suggestion | Why |
| Security professional moving into cloud with 5 years of experience | CCSP is a strong fit | It matches the experience requirement and the cloud focus |
| Already hold CISSP | CCSP is a natural next credential | One source says an active CISSP waives the CCSP experience requirement. See CISSP vs CISM to compare broader paths |
| Under 5 years of experience | Consider CCSK first | See our CCSK vs CCSP comparison |
| Working mainly in AWS | Compare CCSP with a vendor credential | See CCSP vs AWS Security Specialty |
| Early in your career | Look at entry points first | See our best cybersecurity certifications ranking |
| Interested in offensive security | CCSP is not the best match | Compare with CISSP vs CEH |
If You Studied Before August: The Gap Table
| Gap | What to add | Where it lives |
| AI and ML in reference architecture | The impact of AI and ML on cloud design | Subdomain 1.2 |
| AI/ML as a topic | Threat detection, SOAR, ethics and regulatory requirements | Subdomain 1.6 |
| AI/ML data protection | Dataset and model privacy and security | Subdomain 2.9 |
| OWASP lists | OWASP API Top 10 and OWASP Top 10 for LLM Applications | Subdomain 4.1 |
| AI-based monitoring | How AI supports SOC, SIEM and incident response | Subdomain 5.6 |
| Reported extras | Zero trust, SBOMs, containers, EU AI Act, NIS2, DORA | Reported by third parties, not named as subdomains |
ISC2 does not publish a line-by-line redline between the two outlines, so this table combines ISC2’s current outline with third-party comparisons of the old and new versions. If your study material predates the outline, the gap is about five specific items. You do not need to restart your preparation.
An Eight Week Study Plan
This plan assumes you already work in security and have some cloud exposure.
| Week | Focus | Goal |
| 1 | Domain 1 | Cloud concepts, reference architecture, provider evaluation, and the AI/ML subdomains |
| 2 | Domain 2 | Data lifecycle, encryption, key management, classification, and AI/ML data protection |
| 3 | Domain 3 | Infrastructure, risk analysis, controls, continuity |
| 4 | Domain 4 | Secure SDLC, testing methods, and the OWASP API and LLM lists |
| 5 | Domain 5 | Operations, forensics, controls and standards, and AI-based monitoring |
| 6 | Domain 6 | Legal, privacy, audit, risk and contracts |
| 7 | Adaptive practice | Answer one question at a time and review every miss |
| 8 | Weak spots and rest | Revisit your lowest area and book the exam |
For extra practice, our CCSP practice questions can supplement your own notes, as long as you check each topic against ISC2’s outline.
Five practice prompts from the new outline
These are study prompts, not real exam questions.
| # | Prompt | Subdomain |
| 1 | A team wants to train a model on customer data in a public cloud. List three data protection controls you would require | 2.9 |
| 2 | Name two risks in the OWASP Top 10 for LLM Applications and one mitigation for each | 4.1 |
| 3 | Explain how AI-based monitoring could help a SOC, and one risk of relying on it | 5.6 |
| 4 | Compare two cloud providers for hosting an AI workload, and state the security criteria you would use | 1.5 and 1.2 |
| 5 | Describe the ethical and regulatory questions to ask before deploying an AI tool for threat detection | 1.6 |
Common Mistakes
| Mistake | Why it hurts |
| Studying only from pre-August material | You will miss five specific AI-related items |
| Overreacting to a one-point weight change | The shift in Domains 4 and 5 is tiny |
| Memorizing every “reported only” topic | They are not named as subdomains. Prioritize confirmed items |
| Ignoring the OWASP API and LLM lists | They are named in subdomain 4.1 |
| Skipping Domain 6 because it is the smallest | It is still a reported 13% |
| Forgetting you cannot revisit adaptive questions | Pace yourself and commit to each answer |
| Assuming the fee and waiver rules are official | Confirm them on ISC2’s site |
| Treating narrative AI text as guaranteed objectives | It is commentary unless ISC2 confirms |
Career Value
CCSP targets security professionals who design, manage and secure cloud environments, and ISC2’s own workforce research says cloud security is among the most in-demand skills. The updated outline adds AI security topics, which keeps the credential aligned with where cloud work is heading.
We have not included salary figures in this post. We could not find a figure that separates people holding CCSP from everyone else in a similar cloud security role. If you are comparing paths, our best cybersecurity certifications ranking compares credentials by return on investment.
What We Don’t Know Yet
| Open question | Why it matters |
| The official domain weights | We rely on third-party sources that agree with each other |
| Whether the reported extras (zero trust, SBOMs, NIS2, DORA) are tested | They are not named as subdomains |
| The official question count, time and fee | ISC2’s pages as we read them did not state them |
| How the pass rate changes under the new outline | No data published |
| Whether the narrative AI text produces scored questions | ISC2 does not say |
| Whether weights will shift again | Outlines can change |
| How ISC2 treats candidates who tested under the old outline and failed | We found no statement |
FAQS
When did the CCSP exam outline change?
The revised outline is dated August 1, 2026 on ISC2’s outline page, and ISC2 announced it in June 2026.
Did the CCSP domains change?
No. The six domain names are the same: Cloud Concepts, Architecture and Design; Cloud Data Security; Cloud Platform and Infrastructure Security; Cloud Application Security; Cloud Security Operations; and Legal, Risk and Compliance.
Did the domain weights change?
Barely. Two third-party sources report Cloud Application Security falling from 17% to 16% and Cloud Security Operations rising from 16% to 17%. ISC2’s page did not show the weights we could read.
What is new in the CCSP outline?
AI and ML content appears in subdomains 1.2, 1.6, 2.9 and 5.6, and subdomain 4.1 names the OWASP API Top 10 and the OWASP Top 10 for LLM Applications.
Does the CCSP exam cover agentic AI?
The word does not appear in the enumerated subdomains we read, so we cannot say it is tested.
Is zero trust on the CCSP exam?
Some third-party sources list it as a distinct topic, but it is not an enumerated subdomain on ISC2’s page. Study it as general cloud security knowledge.
How many questions are on the CCSP exam?
Third-party sources report 100 to 150 questions in up to 3 hours using computerized adaptive testing, with about 125 typical. Check ISC2’s exam policy page for the official numbers.
What is the passing score?
700 out of 1,000, according to the sources we read.
How much does the CCSP exam cost?
One source reports $599 per attempt in the Americas and a $125 annual maintenance fee. Confirm current pricing with ISC2.
How much experience do I need?
ISC2’s CCSP page lists 5 years of required work experience. Third-party sources break it down as three years in information security and one year in a CCSP domain, with waivers for a degree, CCSK or an active CISSP.
Can I take CCSP without the experience?
One source says you can pass the exam and become an Associate of ISC2, with six years to meet the requirement. Confirm this with ISC2.
Do I need to restart if I studied before August?
No. Add the AI and ML items, the OWASP API and LLM lists, and AI-based monitoring. The rest of your preparation still applies.
How does CCSP compare with CCSK?
CCSP is a professional-level credential with a work experience requirement, while CCSK is often a first step. Our CCSK vs CCSP guide compares them in detail.